

Framework Security Introduces Agentic Third-Party Risk Management to Accelerate Vendor Security Reviews
New agentic capabilities help organizations evaluate vendor security evidence, identify risk, and make defensible third-party decisions without weeks of manual review.
LOS ANGELES — September 24, 2026— Framework Security today announced the introduction of its Agentic Third-Party Risk Management (TPRM) capability, designed to help organizations assess vendor security risk faster while maintaining human oversight and accountability.
Third-party risk reviews have traditionally required security teams to manually collect questionnaires, SOC 2 reports, penetration testing results, policies, certifications, and other documentation before determining whether a vendor meets the organization's security requirements.
As vendor ecosystems grow, that process becomes increasingly difficult to scale.
Framework Security is changing the way that work gets done.
The company's agentic TPRM approach uses AI agents to assist throughout the vendor assessment lifecycle—from evidence collection and analysis through risk identification and follow-up—while Framework Security professionals remain responsible for reviewing findings and providing security guidance.
Moving Beyond the Security Questionnaire
Traditional third-party assessments often rely heavily on what a vendor says about its own security program.
Framework Security's approach is designed to evaluate the evidence behind those answers.
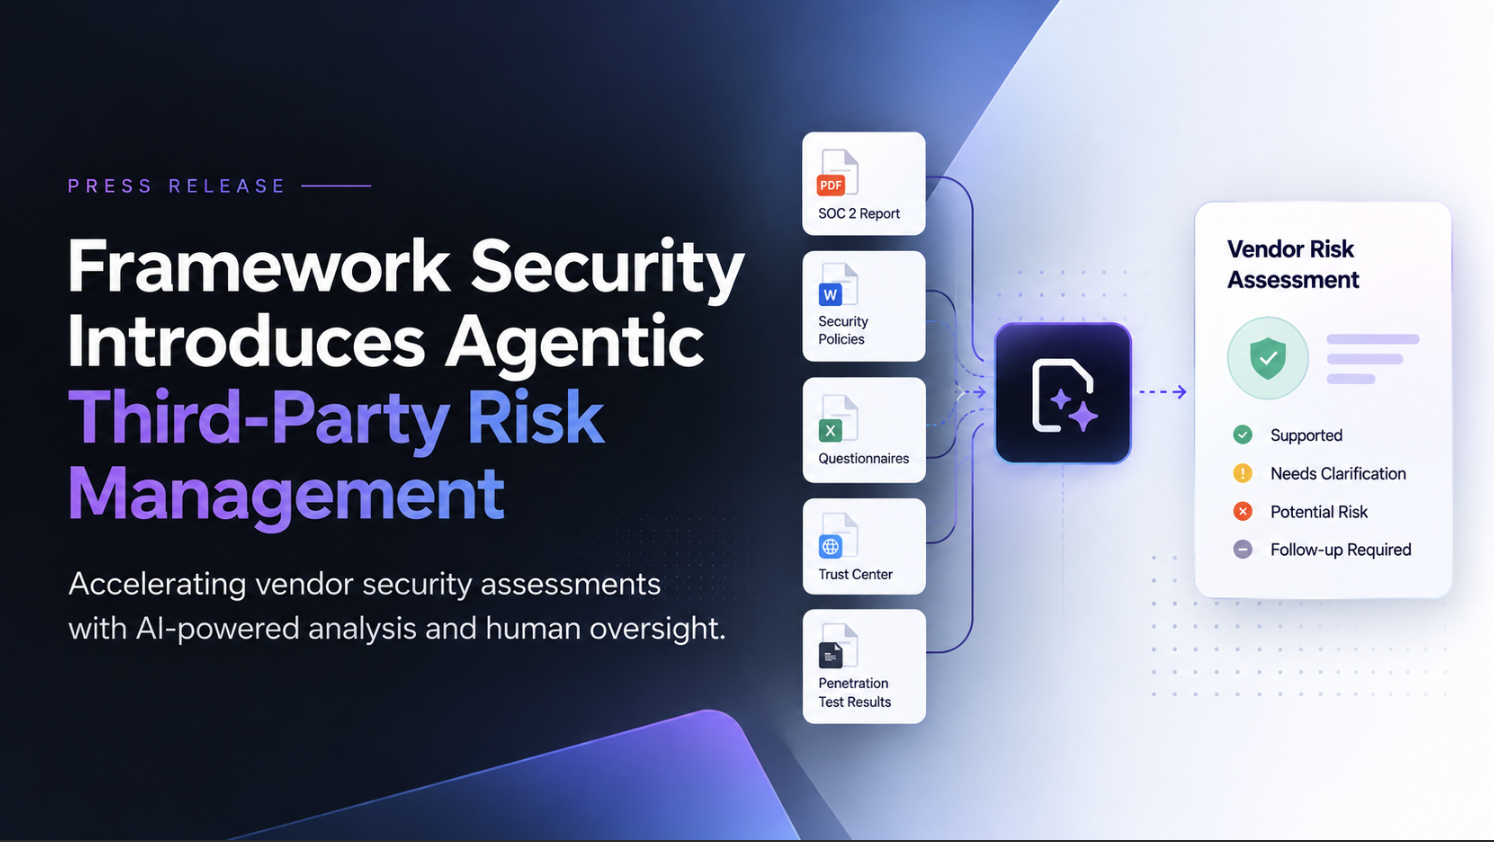
The agentic workflow can analyze available vendor security documentation, including policies, audit reports, certifications, penetration testing documentation, security questionnaires, and other supporting evidence.
That evidence can then be evaluated against defined security requirements to determine where controls are supported, where additional evidence is needed, and where potential risks require human review.
The objective is not simply to complete questionnaires faster.
It is to give organizations a clearer answer to a more important question:
Do we have enough evidence to understand and accept the risk of doing business with this vendor?
How Agentic TPRM Works
Framework Security's agentic workflow is designed to support the repetitive and time-intensive portions of vendor risk management while escalating decisions requiring professional judgment.
The process can assist with:
- Collecting and organizing vendor security evidence
- Reviewing policies, certifications, audit reports, questionnaires, and supporting documentation
- Evaluating evidence against established security requirements
- Identifying missing, incomplete, or conflicting evidence
- Generating targeted follow-up questions
- Highlighting potential security risks requiring further investigation
- Producing structured assessment findings and supporting evidence
- Maintaining a documented record of how vendor risk decisions were reached
Rather than requiring an analyst to begin every assessment from a blank page, the agent performs much of the initial evidence analysis and presents the results for professional review.
AI Accelerates the Review. Humans Own the Decision.
Framework Security's approach is built around a simple principle:
Delivery speed is a risk decision—and someone has to own it.
Businesses need to adopt new technology quickly. Procurement teams need to onboard vendors. Security teams need enough evidence to understand the risk those vendors introduce.
Those objectives should not have to compete.
Agentic TPRM is designed to compress the time required to gather and analyze information without transferring accountability for the decision to an AI system.
Framework Security professionals review findings, investigate material gaps, challenge questionable evidence, and help organizations understand the business implications of identified risks.
AI accelerates the work.
Humans remain accountable for the risk decision.
Bringing Security Into the Decision Earlier
Third-party security concerns are often discovered too late—after procurement has selected a vendor, contracts are being finalized, or technology has already been introduced into the environment.
Framework Security's Agentic TPRM capability is designed to move that analysis earlier in the process.
Because:
The business should hear about tradeoffs early, not at the incident review.
Faster assessments give security teams an opportunity to identify meaningful risks without unnecessarily slowing the business.
Instead of treating third-party risk management as a compliance exercise, organizations can use it as part of the decision-making process itself.
A More Scalable Model for Third-Party Risk
The goal of agentic TPRM isn't to eliminate security professionals.
It's to eliminate the hours they spend doing work that doesn't require their judgment.
By automating evidence organization, initial analysis, gap identification, and other repeatable activities, Framework Security can focus professional expertise on the areas where it matters most: interpreting risk, challenging assumptions, understanding business context, and determining what should happen next.
The result is a third-party risk program designed to be faster, more consistent, evidence-driven, and defensible.
About Framework Security
Framework Security is a cybersecurity consulting firm helping organizations understand, manage, and reduce security risk through strategic security guidance, risk and compliance assessments, penetration testing, incident response, AI governance, and security program development.
Framework Security works alongside organizations to translate technical security risk into practical business decisions—helping leadership understand not only where risk exists, but what to do about it.


Talk With A Cybersecurity Expert
Bring the deadline you're staring at, the framework you're being held to, and the team you have. In 30 minutes we'll tell you honestly whether we're the right fit — and if we are, what the first two weeks look like.
Book a working session