Critical Security Controls Assessment
Know Exactly Where Your Security Program Stands Today
The CIS 18 Critical Security Controls give you a prioritized, action-oriented baseline. Framework Security assesses your environment against all 153 safeguards — then delivers a clear roadmap to close gaps fast.

The Problem
You Can't Fix What You Haven't Measured Against a Standard
Most mid-market organizations know they have security gaps but lack a structured way to find them. Without a baseline assessment, budget goes to the wrong priorities and real risk stays hidden.
The Solution
A Prioritized Assessment Mapped to Your Maturity Level
We evaluate your controls across all three CIS Implementation Groups — IG1 through IG3 — scoring each safeguard, identifying what's missing, and building a phased remediation plan tied to your risk profile.
Threats Stopped Before They Become Incidents
Attackers are detected and contained early, long before they can move laterally, exfiltrate data, or cause damage. Your business keeps running while threats are neutralized quietly in the background.
Full Visibility Into Your Security Environment
A real-time view of what's happening across your endpoints, network, and cloud — all in one place. Nothing hides in a blind spot because everything is being watched, correlated, and analyzed continuously.
Faster Recovery When Incidents Occur
When something does happen, a practiced response team mobilizes immediately with full context of your environment already in hand. Downtime and damage are minimized because the plan exists long before the breach does.
Ongoing Risk Reduction Over Time
Vulnerabilities are tracked and closed on a continuous cycle, so your attack surface shrinks steadily rather than staying static. Leadership gets measurable proof that security is improving, not just maintained.
Reduced Burden on Your Internal Team
Your IT and security staff stop drowning in alerts and can focus on strategic work instead of reactive firefighting. We handle the noise, the triage, and the response so your team operates without burnout.
Confidence to Grow Without Outpacing Your Security
As your business adds users, systems, and complexity, your security coverage scales automatically with it. You never face a situation where growth has left you exposed.
Benefits
Build a Security Program That Scales with Your Business
CIS maps directly to NIST, PCI DSS, HIPAA, and more. Framework's vendor-agnostic approach means recommendations that fit your environment — not a product pitch disguised as an assessment.
Round-the-Clock Threat Coverage
Attackers don't work business hours, and neither do we — your environment is monitored continuously by experienced analysts. No gap in coverage means no window of opportunity for threats to go undetected.
Faster Incident Detection & Response
Our analysts cut through alert noise to identify real threats quickly, reducing the dwell time attackers have in your environment. Faster detection directly limits the blast radius of any security incident.
Scalable Security Without Added Headcount
You get the capabilities of a full security operations team without the cost and complexity of hiring one in-house. As your organization grows, our services scale with you seamlessly.
Our Reviews
What senior operators say after we ship.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.

"Navigating AI regulation is a moving target. They provided the deep regulatory expertise and proactive guardrails we needed to innovate."

Jeff Neuman, SVP, AI Data & Engineering, Lender Toolkit
"Framework Security establishes a seamless workflow. The team is attentive, communicative, and pragmatic."
Aaron Scruggs, CEO, Rephyr
"If you need to always have a team of go-to security experts, they should be on your shortlist."
Daniel Klingenberg, Information Security Director, Building Zone Industries
"I wish I had found Framework before speaking with any other companies."
Ben Londa, President & CEO, Volo Solutions

"Framework has an uncanny ability to make the highly complex simple to understand."
Tyler Vaughn, Chief Technology Officer, Whitetail Properties
"They know how to execute. They will drill down to find the right solutions to close the gaps and implement that plan."
Jason White, Vice President, HP | Vyopta

How We Work
The embedded model. Three steps. No PDFs left behind.
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from the first call to the last.
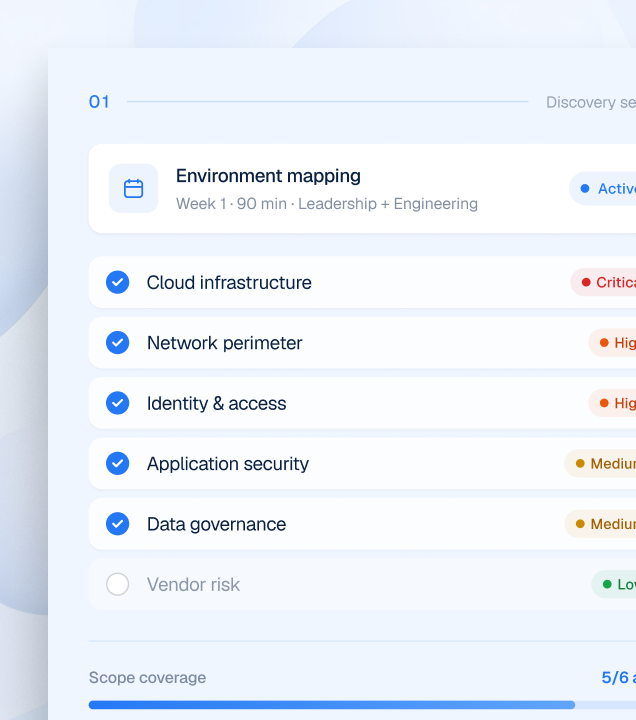
Scope what matters
A working session with your leadership and engineering teams to map your environment, risk priorities, and audit timeline. Not a sales discovery call.
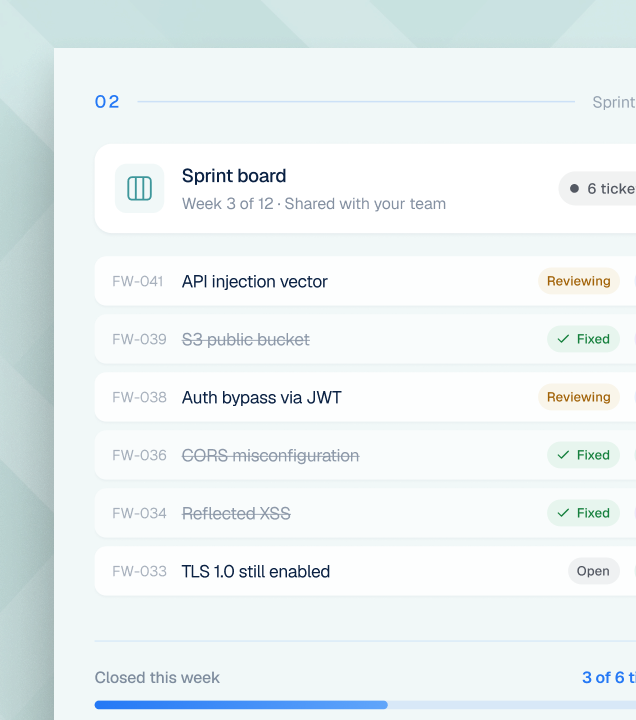
Embed with your team
Weekly working sessions. Shared ticketing. Engineers paired with yours. Findings become tickets, tickets become fixes — in the same week, not the same quarter.
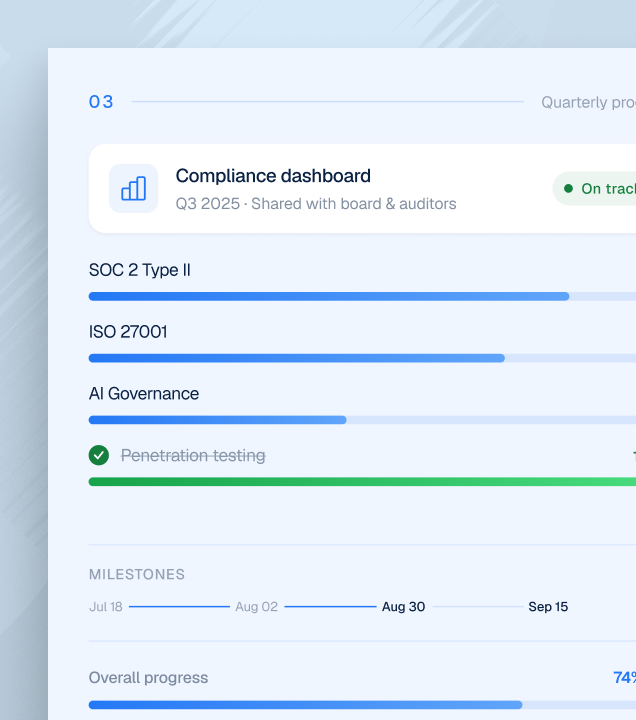
Keep the work moving
Ongoing retainer support across compliance, testing, and AI governance. Your auditors, board, and customers see real progress every quarter.
Why Companies choose Framework Security
Protecting over $20B in assets nationally
Leadership Experience | 65+ years of combined team experience across real enterprise environments, not junior analysts overseen from a distance. |
Independent And Vendor-Agnostic | We recommend what fits your environment, your stage, and your budget. Even when "fit" means using less than what a vendor would sell you. Our only product is the work. |
Compliance Philosophy | Frameworks are treated as living tools that scale with your business, not static checklists built to pass audits and collect dust. |
Executive Access | vCISO services give you direct access to senior security leadership, bridging the gap between board-level priorities and technical execution. |
Pricing & Value | Partner pricing passed directly to clients. Purpose-built for mid-market organizations that need enterprise-grade security without enterprise-grade overhead. |
Third-Party Recognition | Clutch #1 in North America, G2 Top 10, AWS Marketplace top pen testing provider, Gartner Peer Insights listed, validated across multiple independent platforms. |
Case Studies
Done-for-you compliance


FAQs
Everything you need to know before you start
Don't see yours? Send a note — you'll hear back from a real person, usually within a business day.
What does Framework Security do?
We are a cybersecurity and virtual CISO (vCISO) advisory firm. We build and run security programs for companies that need to protect sensitive data and prove it to regulators, auditors, and clients, but do not have a full security team of their own. That covers penetration testing, SOC 2 and CMMC compliance, NIST 800-171, AI security and governance, and ongoing security leadership. We do not hand you a checklist and wish you luck. We build the program, get you where you need to be, and make sure you stay there.
Who do you work with?
Organizations that carry real accountability for security but are not primarily security companies. Two we know especially well: construction and defense contractors who need CMMC certification, and fintech and regulated firms who need SOC 2, AI governance, or answers for a board, a regulator, or a client's due-diligence team. Beyond those, we support SMB and mid-market companies who simply need a security program that holds up. If you are the person who is accountable when something goes wrong, and you do not have a dedicated security org behind you, you are who we built this for.
What is a vCISO, and why not just hire a CISO?
A vCISO is executive-level security leadership embedded in your operations, backed by a full team, without the full-time salary. A full-time CISO runs $200,000 to $300,000 or more a year, plus 12 to 18 months to hire and ramp. Our vCISO gives you that same leadership at a fraction of the cost, from a team that has built programs for firms managing over $20 billion in assets.
Which compliance frameworks and standards do you handle?
The ones our clients are actually held to: CMMC and NIST 800-171 for federal and defense work, SOC 2 for proving security to customers, and ISO 42001 for AI governance. We also run the work underneath the certifications: penetration testing, infrastructure audits, documentation, and the real technical controls auditors expect. If you are not sure which applies to you, that is one of the first things we sort out.
We're not sure where we stand. How do we get started?
With a free, confidential assessment. We review your environment, map it against the standard that applies to you, and give you a plain-English picture of what you have, what you are missing, and what it takes to close the gap. About 30 to 60 minutes, and you leave knowing exactly where you stand, whether or not you work with us.
How much does this cost?
It depends on what you need, so we scope pricing to your environment rather than publishing a number that fits no one. Plainly: our vCISO engagements cost a fraction of a full-time hire, and we offer fixed-scope entry points, such as a one-week AI security audit starting at $2,500. Your free assessment ends with a clear scope and a straight number, not a surprise later.
How long does it take?
For full compliance programs, typically 60 to 90 days to audit-ready, depending on where you start. Scoped engagements move faster, a focused audit in about a week. We give you a realistic timeline after the assessment, because we would rather be accurate than optimistic.
What makes Framework Security different?
We specialize, so you get understanding instead of a generic template. We deploy real protections and build the documentation auditors ask for, not policies that look good and protect nothing. And we treat you like a competent adult being handed real information, not a prospect to scare. Firms managing over $20 billion in assets trust us, we are a G2 Top 10 company and Clutch's number one firm in North America, and our team carries 65-plus years of combined experience.
Start here
A working session.
Not a sales call.
Bring the deadline you're staring at, the framework you're being held to, and the team you have. In 30 minutes we'll tell you honestly whether we're the right fit — and if we are, what the first two weeks look like.