AI Management System Certification
Get Certified. Get Credible. Lead on AI Governance.
ISO 42001 is the global standard for responsible AI management. Framework guides your organization through certification — so you can demonstrate AI accountability to clients, partners, and regulators.
The Problem
AI Without a Standard Leaves You Exposed to Scrutiny
Regulators, enterprise buyers, and investors are demanding proof that AI is managed responsibly. Without a recognized standard, your organization risks losing deals, audits, and stakeholder confidence.
The Solution
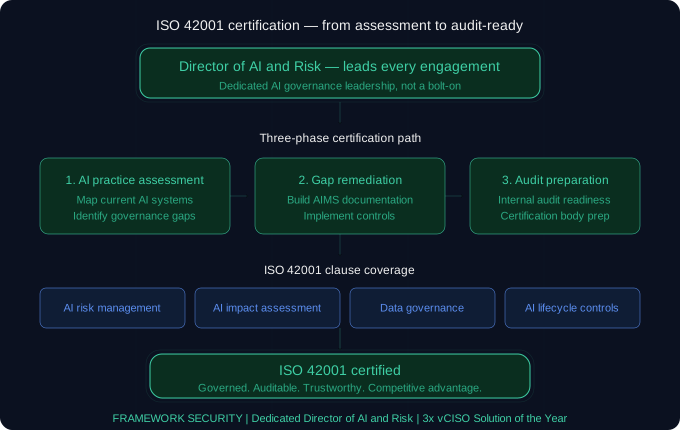
ISO 42001 Certification Support From Assessment to Audit
Framework's AI governance team — led by our dedicated Director of AI and Risk — maps your current AI practices, closes compliance gaps, and prepares your organization for a successful ISO 42001 audit.
Compliance Gap Assessments
We benchmark your current environment against target frameworks to reveal exactly where you fall short. You receive a prioritized remediation roadmap to close those gaps efficiently.
Regulatory Mapping (SOC 2, ISO, HIPAA)
We map your controls and processes directly to the specific frameworks that govern your industry. This eliminates guesswork and redundant work when pursuing multiple certifications.
Continuous compliance monitoring
We implement automated tooling and processes to track your compliance posture on an ongoing basis. Drift from your required controls is flagged immediately rather than discovered at the next annual review.
Risk Register Development
We build a structured, living inventory of your organization's risks, owners, and mitigation statuses. This gives leadership a single source of truth for risk decision-making.
Policy & Procedure Creation
We draft and refine the security policies and operational procedures your organization needs to meet compliance requirements. Documents are written to be actionable, not just box-checking.
Third-Party Vendor Risk Reviews
We assess the security posture of your vendors and partners to ensure they don't introduce risk into your environment. You gain visibility into your extended attack surface, not just your internal one.
Benefits
What ISO 42001 Certification Means for Your Business
Certification signals that your AI systems are governed, auditable, and trustworthy — opening doors with enterprise clients, satisfying regulators, and giving your board defensible AI oversight.
Reduced Risk Exposure
Identify and close gaps before attackers find them — systematically lowering your organization's attack surface.
Proactive Risk Visibility
We surface operational, financial, and cybersecurity risks before they become incidents. Decision-makers get a clear, prioritized view of where the business is most exposed.
Stronger Audit Readiness
Our team ensures your controls, documentation, and evidence are organized and audit-ready at all times. You'll walk into any review with confidence rather than scrambling at the last minute.
Our Reviews
What senior operators say after we ship.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.

"Navigating AI regulation is a moving target. They provided the deep regulatory expertise and proactive guardrails we needed to innovate."

Jeff Neuman, SVP, AI Data & Engineering, Lender Toolkit
"Framework Security establishes a seamless workflow. The team is attentive, communicative, and pragmatic."
Aaron Scruggs, CEO, Rephyr
"If you need to always have a team of go-to security experts, they should be on your shortlist."
Daniel Klingenberg, Information Security Director, Building Zone Industries
"I wish I had found Framework before speaking with any other companies."
Ben Londa, President & CEO, Volo Solutions

"Framework has an uncanny ability to make the highly complex simple to understand."
Tyler Vaughn, Chief Technology Officer, Whitetail Properties
"They know how to execute. They will drill down to find the right solutions to close the gaps and implement that plan."
Jason White, Vice President, HP | Vyopta

How We Work
The embedded model. Three steps. No PDFs left behind.
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from the first call to the last.
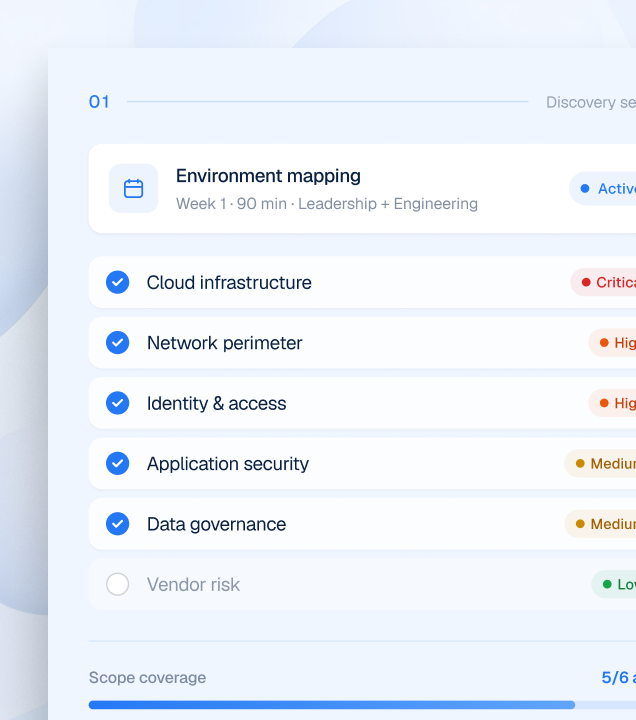
Scope what matters
A working session with your leadership and engineering teams to map your environment, risk priorities, and audit timeline. Not a sales discovery call.
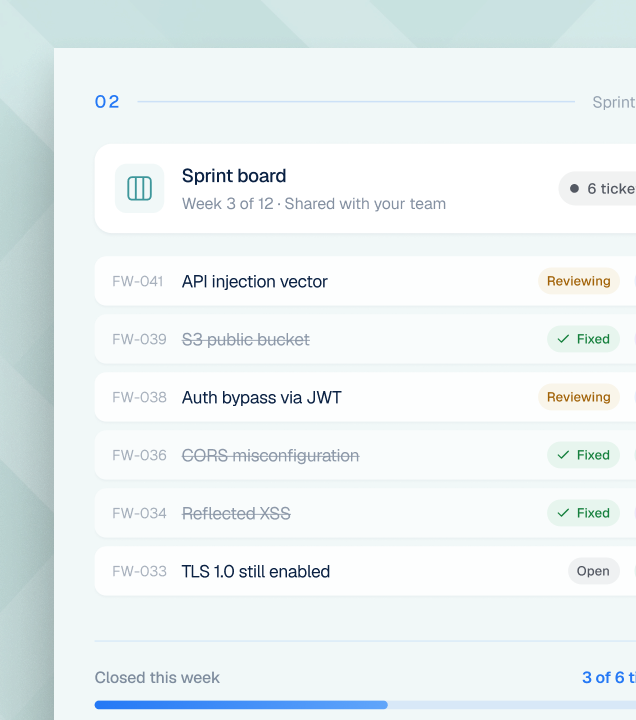
Embed with your team
Weekly working sessions. Shared ticketing. Engineers paired with yours. Findings become tickets, tickets become fixes — in the same week, not the same quarter.
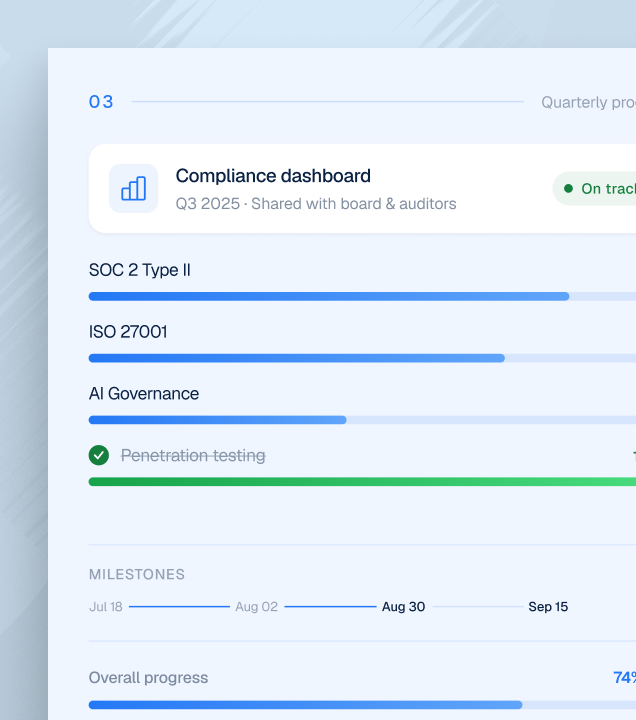
Keep the work moving
Ongoing retainer support across compliance, testing, and AI governance. Your auditors, board, and customers see real progress every quarter.
Why Companies choose Framework Security
Protecting over $20B in assets nationally
Leadership Experience | 65+ years of combined team experience across real enterprise environments, not junior analysts overseen from a distance. |
Independent And Vendor-Agnostic | We recommend what fits your environment, your stage, and your budget. Even when "fit" means using less than what a vendor would sell you. Our only product is the work. |
Compliance Philosophy | Frameworks are treated as living tools that scale with your business, not static checklists built to pass audits and collect dust. |
Executive Access | vCISO services give you direct access to senior security leadership, bridging the gap between board-level priorities and technical execution. |
Pricing & Value | Partner pricing passed directly to clients. Purpose-built for mid-market organizations that need enterprise-grade security without enterprise-grade overhead. |
Third-Party Recognition | Clutch #1 in North America, G2 Top 10, AWS Marketplace top pen testing provider, Gartner Peer Insights listed, validated across multiple independent platforms. |
Case Studies
Done-for-you compliance

FAQs
Everything you need to know before you start
Don't see yours? Send a note — you'll hear back from a real person, usually within a business day.
What does Framework Security do?
We are a cybersecurity and virtual CISO (vCISO) advisory firm. We build and run security programs for companies that need to protect sensitive data and prove it to regulators, auditors, and clients, but do not have a full security team of their own. That covers penetration testing, SOC 2 and CMMC compliance, NIST 800-171, AI security and governance, and ongoing security leadership. We do not hand you a checklist and wish you luck. We build the program, get you where you need to be, and make sure you stay there.
Who do you work with?
Organizations that carry real accountability for security but are not primarily security companies. Two we know especially well: construction and defense contractors who need CMMC certification, and fintech and regulated firms who need SOC 2, AI governance, or answers for a board, a regulator, or a client's due-diligence team. Beyond those, we support SMB and mid-market companies who simply need a security program that holds up. If you are the person who is accountable when something goes wrong, and you do not have a dedicated security org behind you, you are who we built this for.
What is a vCISO, and why not just hire a CISO?
A vCISO is executive-level security leadership embedded in your operations, backed by a full team, without the full-time salary. A full-time CISO runs $200,000 to $300,000 or more a year, plus 12 to 18 months to hire and ramp. Our vCISO gives you that same leadership at a fraction of the cost, from a team that has built programs for firms managing over $20 billion in assets.
Which compliance frameworks and standards do you handle?
The ones our clients are actually held to: CMMC and NIST 800-171 for federal and defense work, SOC 2 for proving security to customers, and ISO 42001 for AI governance. We also run the work underneath the certifications: penetration testing, infrastructure audits, documentation, and the real technical controls auditors expect. If you are not sure which applies to you, that is one of the first things we sort out.
We're not sure where we stand. How do we get started?
With a free, confidential assessment. We review your environment, map it against the standard that applies to you, and give you a plain-English picture of what you have, what you are missing, and what it takes to close the gap. About 30 to 60 minutes, and you leave knowing exactly where you stand, whether or not you work with us.
How much does this cost?
It depends on what you need, so we scope pricing to your environment rather than publishing a number that fits no one. Plainly: our vCISO engagements cost a fraction of a full-time hire, and we offer fixed-scope entry points, such as a one-week AI security audit starting at $2,500. Your free assessment ends with a clear scope and a straight number, not a surprise later.
How long does it take?
For full compliance programs, typically 60 to 90 days to audit-ready, depending on where you start. Scoped engagements move faster, a focused audit in about a week. We give you a realistic timeline after the assessment, because we would rather be accurate than optimistic.
What makes Framework Security different?
We specialize, so you get understanding instead of a generic template. We deploy real protections and build the documentation auditors ask for, not policies that look good and protect nothing. And we treat you like a competent adult being handed real information, not a prospect to scare. Firms managing over $20 billion in assets trust us, we are a G2 Top 10 company and Clutch's number one firm in North America, and our team carries 65-plus years of combined experience.
Start here
A working session.
Not a sales call.
Bring the deadline you're staring at, the framework you're being held to, and the team you have. In 30 minutes we'll tell you honestly whether we're the right fit — and if we are, what the first two weeks look like.