Expert-led. Embedded. Vendor-agnostic.
Investigate. Remediate.
Automate.
Expert-led cybersecurity. Real assessments, weekly working sessions, shared tickets, and our engineers paired with yours.
Trusted across regulated industries — $20B+ in client assets protected.



Why most security work never actually closes risk.
Most firms deliver a report and disappear.
We stay until the findings are closed, no backlog, no repeat audit gaps, no PDF gathering dust.
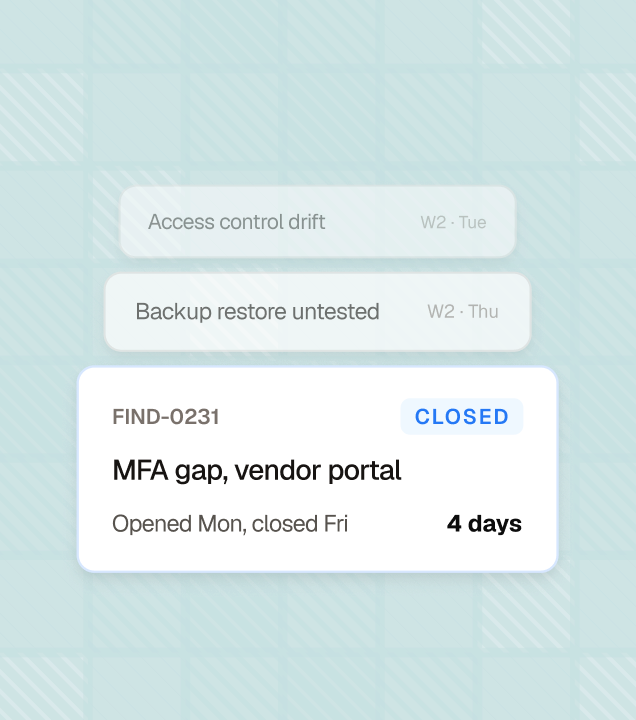
Risk closes in weeks, not quarters.
Findings become tickets. Tickets become fixes. In the same week, not the same quarter.
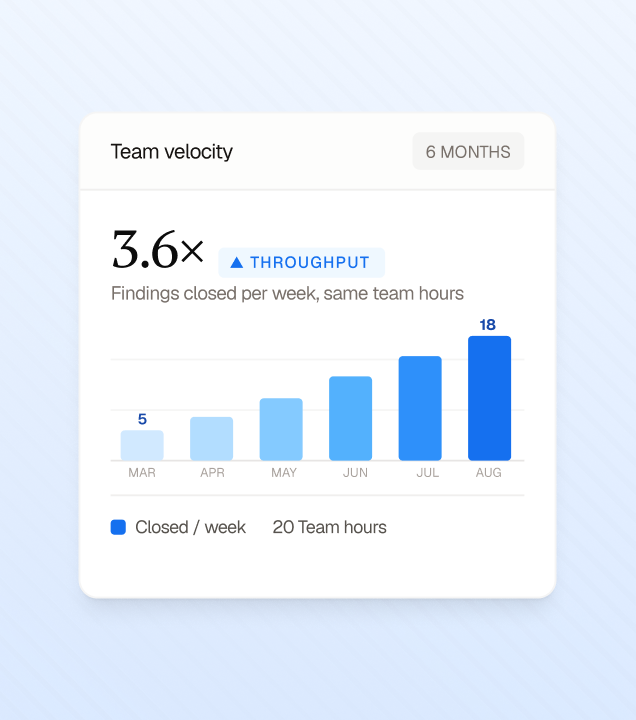
Engineers get faster, not just busier.
We pair with your team instead of dropping work on them. Your people learn the pattern.
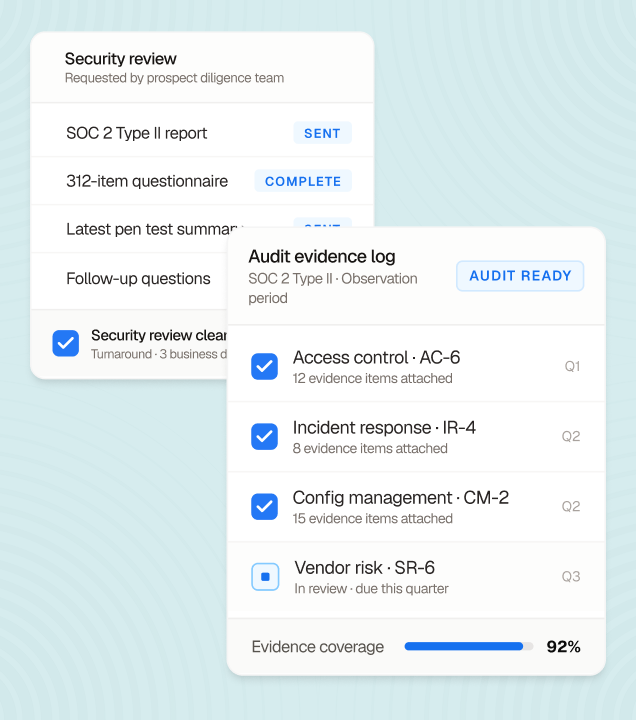
Security spend translates to actual progress.
Auditors, boards, and customers see the work moving every quarter. No more repeat findings.
Three practice areas. One senior team. Real implementation, not slideware.
Every engagement is led by a senior practitioner with 15+ years in the field. We don't hand you off to a junior after the SOW. Our only product is the work.
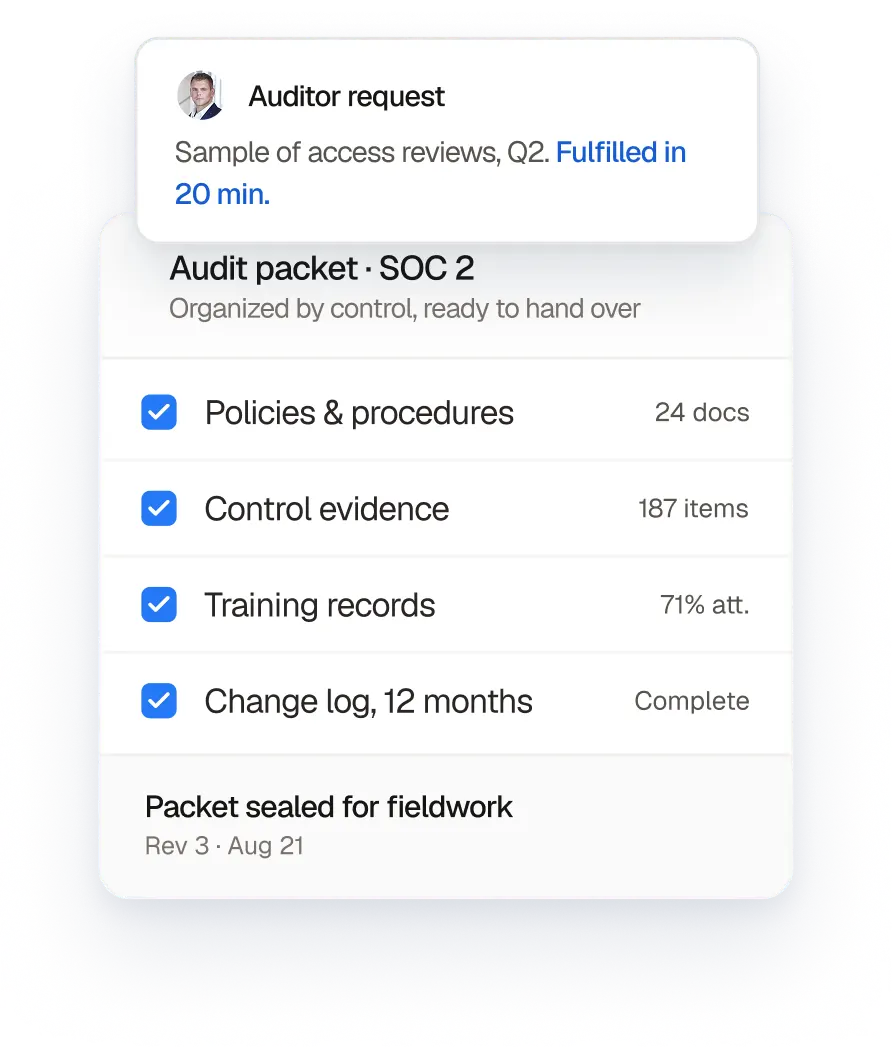
Risk & Compliance
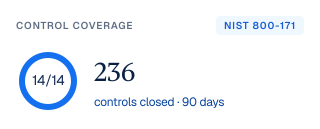
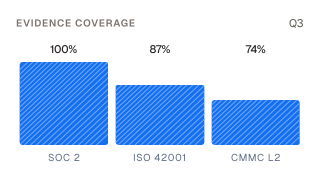
SOC 2, NIST 800-171 / 800-53, CMMC, ISO 42001, and AI governance. We write the policies, stand up the controls, organize the evidence, and sit in the audit meetings with you.
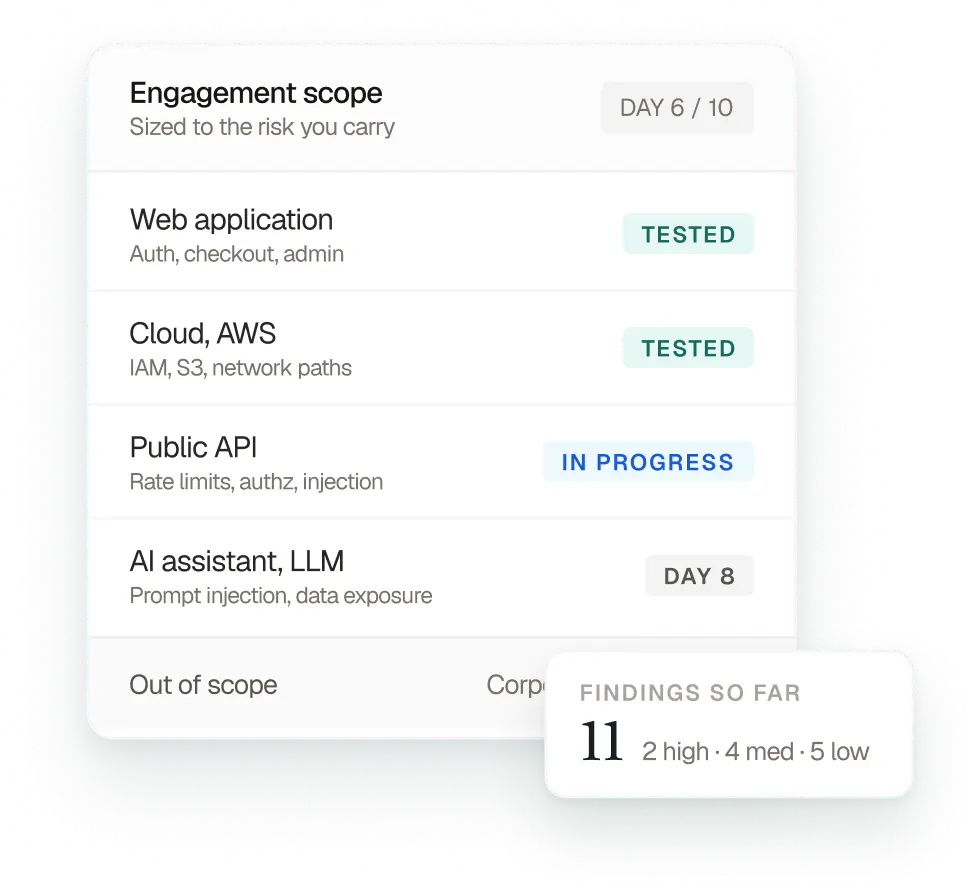
Penetration Testing
Application, cloud, network, API, and AI/LLM testing scoped to the
risk you actually carry. Findings come back as remediation guidance
your engineers can act on, not a wall of red bars.
Managed Security
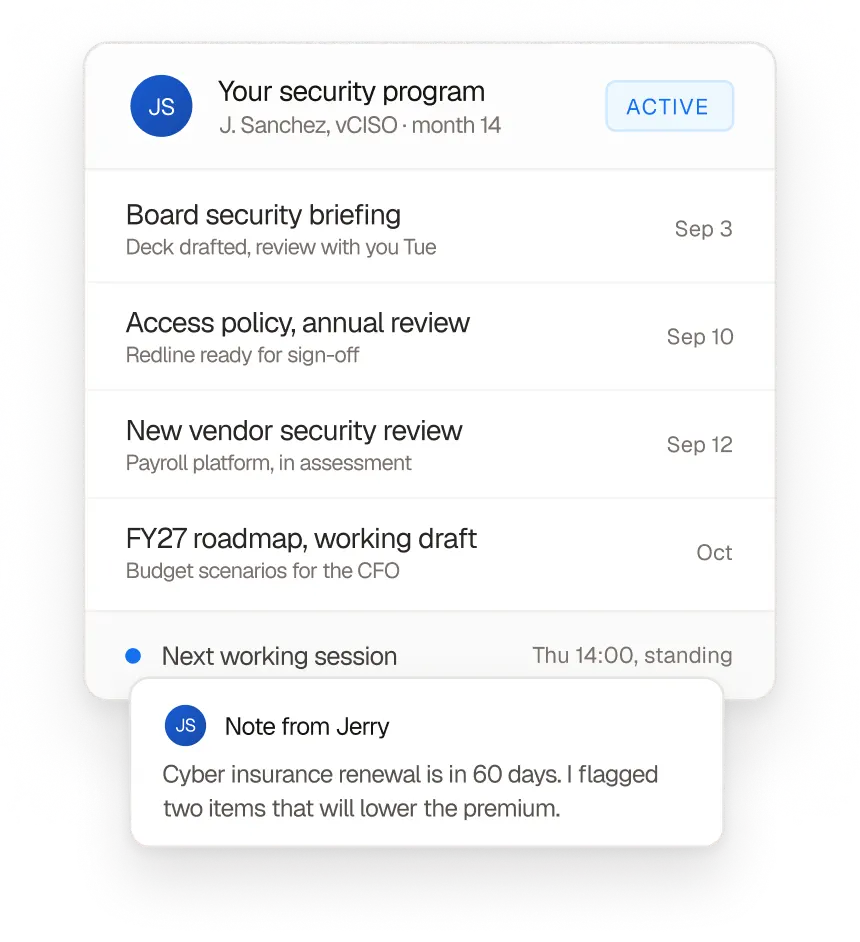
Ongoing coverage across identity, ransomware, incident response,
and executive security leadership. Structured for teams without a
full-time security org.
The embedded model. Three steps. No PDFs left behind.
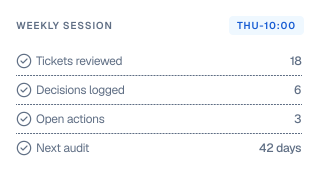
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from the first call to the last.
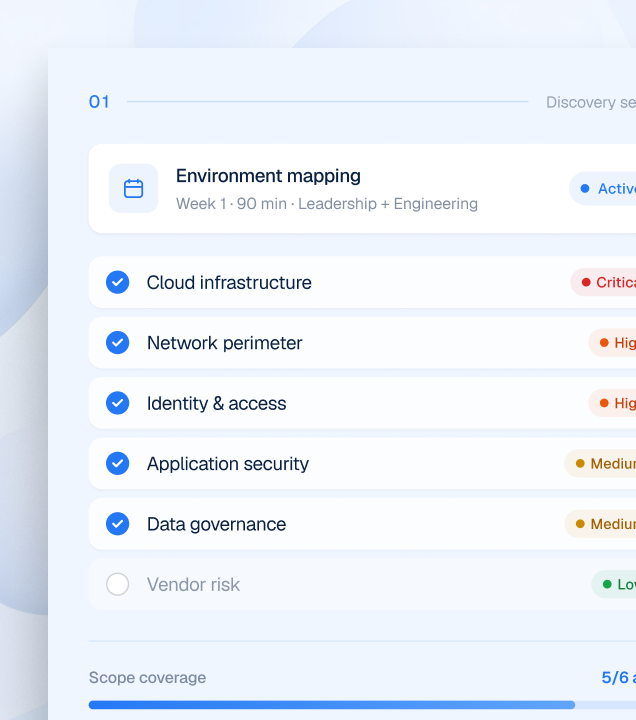
Scope what matters
A working session with your leadership and engineering teams to map your environment, risk priorities, and audit timeline. Not a sales discovery call.
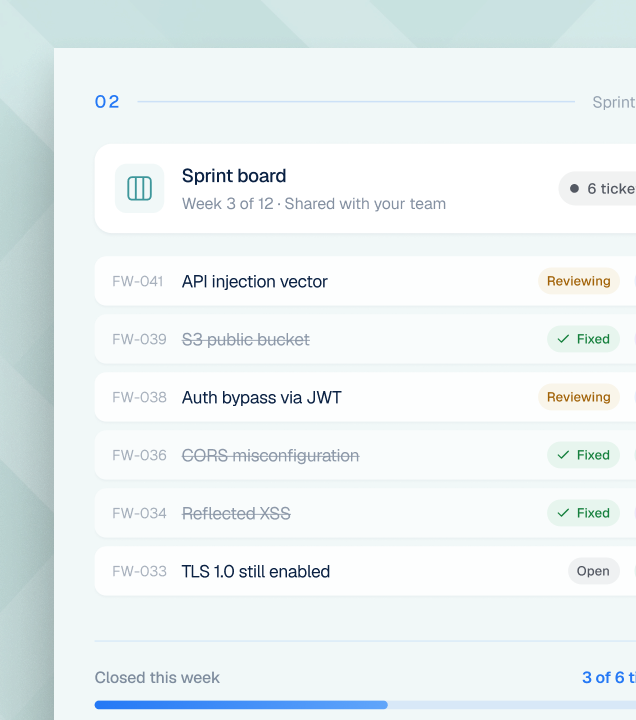
Embed with your team
Weekly working sessions. Shared ticketing. Engineers paired with yours. Findings become tickets, tickets become fixes — in the same week, not the same quarter.
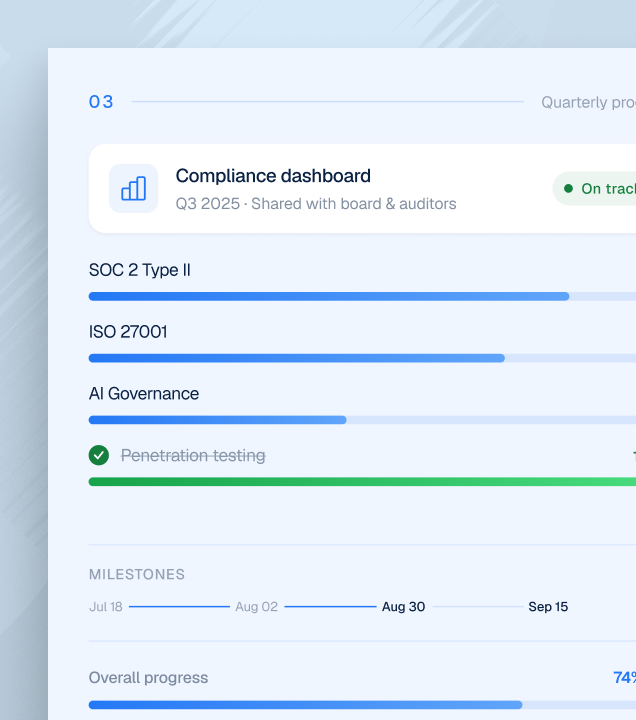
Keep the work moving
Ongoing retainer support across compliance, testing, and AI governance. Your auditors, board, and customers see real progress every quarter.
What "expert-led" actually means when you buy it.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.
Expert Practitioners. Regulated-Industry Depth.
Every Framework engagement is led by expert security practitioners with real experience in the trenches. Not staffed with junior testers running a checklist. 65+ years of combined experience across SOC 2, ISO, and CMMC audits, AI governance reviews, and active incident response.
Responsive On The Timelines That Matter.
Audit deadlines don't move. Incident response windows don't wait. Framework is structured for fast turnaround. Most engagements kick off within two weeks of signature, and embedded clients get same-day response on critical issues.
Independent And Vendor-Agnostic
We recommend what fits your environment, your stage, and your budget. Even when "fit" means using less than what a vendor would sell you. Our only product is the work.
Clear Communicators.
We translate NIST, ISO, and CMMC into language your board, your engineers, and your auditors can all use in the same meeting. Plain English is a deliverable, not a nice-to-have.
The work, in the words of the people we did it for.
Six years of engagements across construction, fintech, healthcare, and AI-first companies. A few representative examples.
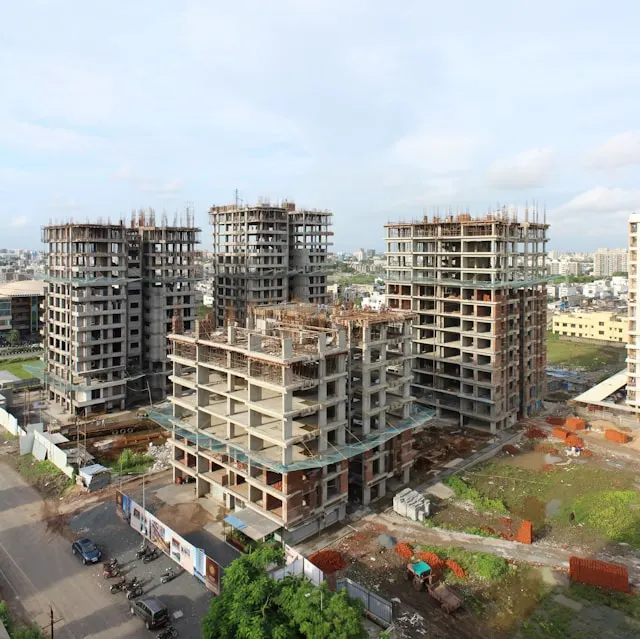
How BZI Construction built a federal-grade cybersecurity program — without hiring a single security employee.
A vCISO engagement delivering NIST 800-171 compliance, CMMC readiness, and real-world protection for a growing construction firm.
A mature vCISO engagement, AI governance included.
The Framework Security–LTK partnership showcases the full power of a mature vCISO engagement — ongoing coverage plus ISO/IEC 42001-aligned AI governance.
A five-year partnership in security, trust, and growth.
A five-year embedded engagement — the kind of retainer relationship the model was designed to sustain.
Built for regulated environments where the answer needs to hold up.
Nine industries. Same model.
Vertical-specific playbooks.


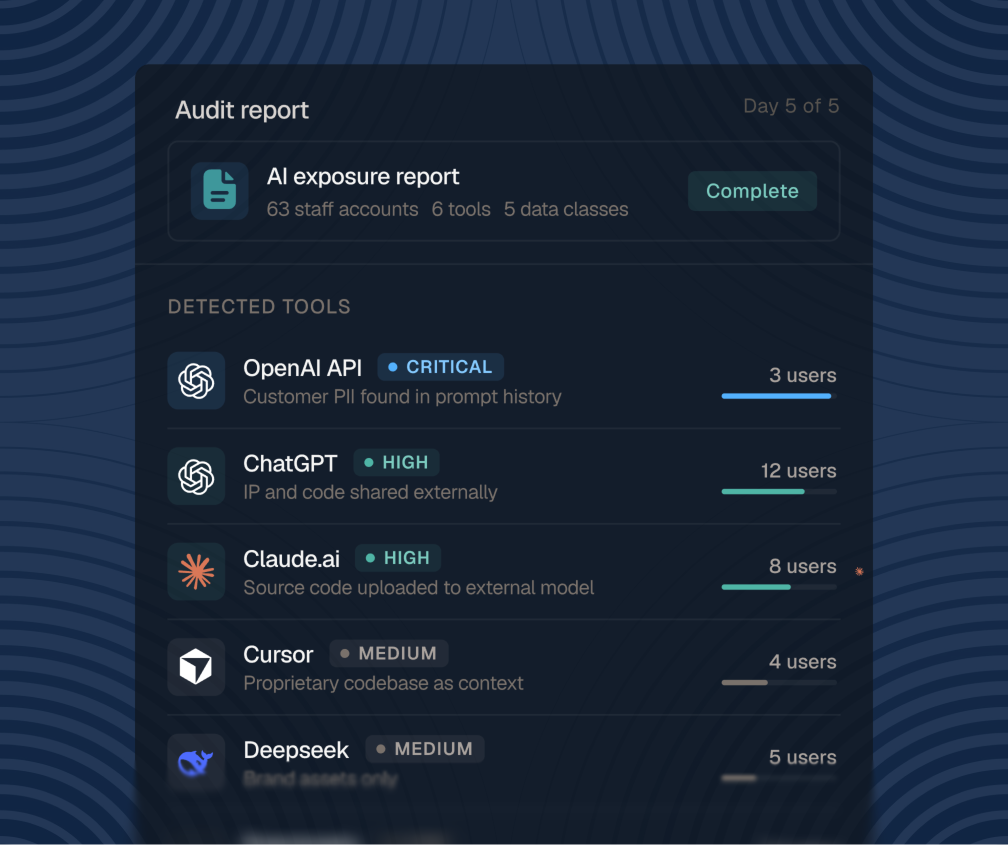
Shadow AI Audit.
One week, fixed scope.
A paid diagnostic for regulated or regulated-adjacent teams that don't yet know which AI tools their staff are using — or what data those tools have seen. Written report, risk scorecard, done in five business days.
The senior operator on your account is on this page too.
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from thefirst call to the last.


What senior operators say after we ship.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.

"Navigating AI regulation is a moving target. They provided the deep regulatory expertise and proactive guardrails we needed to innovate."

Jeff Neuman, SVP, AI Data & Engineering, Lender Toolkit
"Framework Security establishes a seamless workflow. The team is attentive, communicative, and pragmatic."
Aaron Scruggs, CEO, Rephyr
"If you need to always have a team of go-to security experts, they should be on your shortlist."
Daniel Klingenberg, Information Security Director, Building Zone Industries
"I wish I had found Framework before speaking with any other companies."
Ben Londa, President & CEO, Volo Solutions

"Framework has an uncanny ability to make the highly complex simple to understand."
Tyler Vaughn, Chief Technology Officer, Whitetail Properties
"They know how to execute. They will drill down to find the right solutions to close the gaps and implement that plan."
Jason White, Vice President, HP | Vyopta

Recognized by the industry that grades cybersecurity firms.




Everything you need to know before you start
Don't see yours? Send a note — you'll hear back from a real person, usually within a business day.
We are a cybersecurity and virtual CISO (vCISO) advisory firm. We build and run security programs for companies that need to protect sensitive data and prove it to regulators, auditors, and clients, but do not have a full security team of their own. That covers penetration testing, SOC 2 and CMMC compliance, NIST 800-171, AI security and governance, and ongoing security leadership. We do not hand you a checklist and wish you luck. We build the program, get you where you need to be, and make sure you stay there.
Organizations that carry real accountability for security but are not primarily security companies. Two we know especially well: construction and defense contractors who need CMMC certification, and fintech and regulated firms who need SOC 2, AI governance, or answers for a board, a regulator, or a client's due-diligence team. Beyond those, we support SMB and mid-market companies who simply need a security program that holds up. If you are the person who is accountable when something goes wrong, and you do not have a dedicated security org behind you, you are who we built this for.
A vCISO is executive-level security leadership embedded in your operations, backed by a full team, without the full-time salary. A full-time CISO runs $200,000 to $300,000 or more a year, plus 12 to 18 months to hire and ramp. Our vCISO gives you that same leadership at a fraction of the cost, from a team that has built programs for firms managing over $20 billion in assets.
The ones our clients are actually held to: CMMC and NIST 800-171 for federal and defense work, SOC 2 for proving security to customers, and ISO 42001 for AI governance. We also run the work underneath the certifications: penetration testing, infrastructure audits, documentation, and the real technical controls auditors expect. If you are not sure which applies to you, that is one of the first things we sort out.
With a free, confidential assessment. We review your environment, map it against the standard that applies to you, and give you a plain-English picture of what you have, what you are missing, and what it takes to close the gap. About 30 to 60 minutes, and you leave knowing exactly where you stand, whether or not you work with us.
It depends on what you need, so we scope pricing to your environment rather than publishing a number that fits no one. Plainly: our vCISO engagements cost a fraction of a full-time hire, and we offer fixed-scope entry points, such as a one-week AI security audit starting at $2,500. Your free assessment ends with a clear scope and a straight number, not a surprise later.
For full compliance programs, typically 60 to 90 days to audit-ready, depending on where you start. Scoped engagements move faster, a focused audit in about a week. We give you a realistic timeline after the assessment, because we would rather be accurate than optimistic.
We specialize, so you get understanding instead of a generic template. We deploy real protections and build the documentation auditors ask for, not policies that look good and protect nothing. And we treat you like a competent adult being handed real information, not a prospect to scare. Firms managing over $20 billion in assets trust us, we are a G2 Top 10 company and Clutch's number one firm in North America, and our team carries 65-plus years of combined experience.
A working session.
Not a sales call.
Bring the deadline you're staring at, the framework you're being held to, and the team you have. In 30 minutes we'll tell you honestly whether we're the right fit — and if we are, what the first two weeks look like.