Expert-Led Pentesting
Find it. Fix it.
Verify it's gone.
Expert-led penetration testing with real exploitation by senior testers and findings that come back as remediation guidance your engineers can act on.
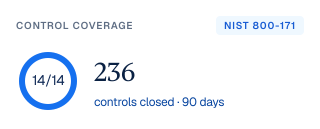
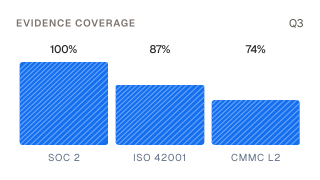
Trusted across regulated industries — $20B+ in client assets protected.



Why most penetration tests never actually close risk.
Most firms run a scan, hand you a report, and disappear. The findings land in a backlog, nobody has time to work them, and next year's test finds the same holes. You paid to learn you're exposed, twice.
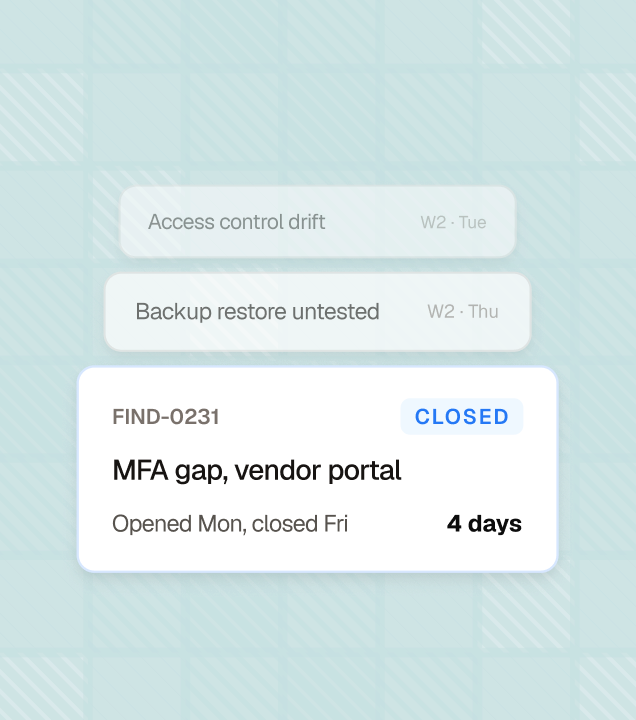
Risk closes in weeks, not quarters.
Findings become tickets. Tickets become fixes. We retest and confirm, in the same engagement, not the next audit cycle.
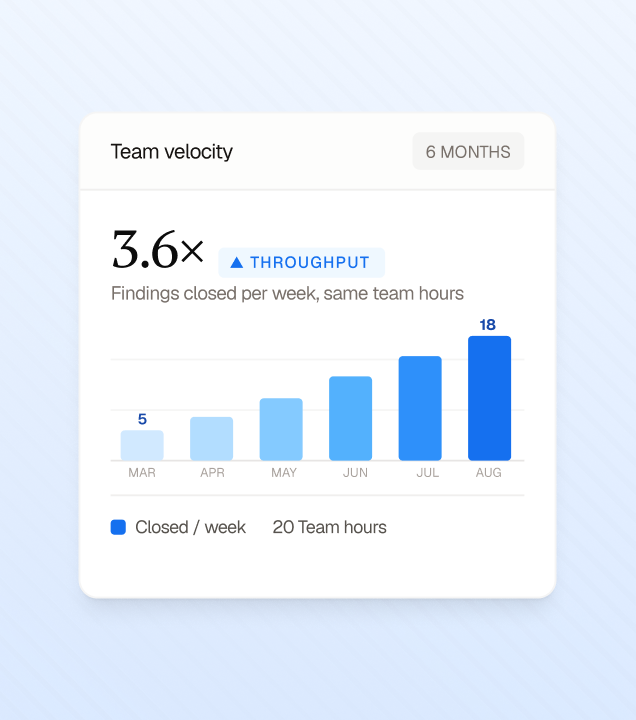
Engineers get faster, not just busier.
We walk your team through the exploit path, not just the CVE. Your people learn to spot the pattern before we do.
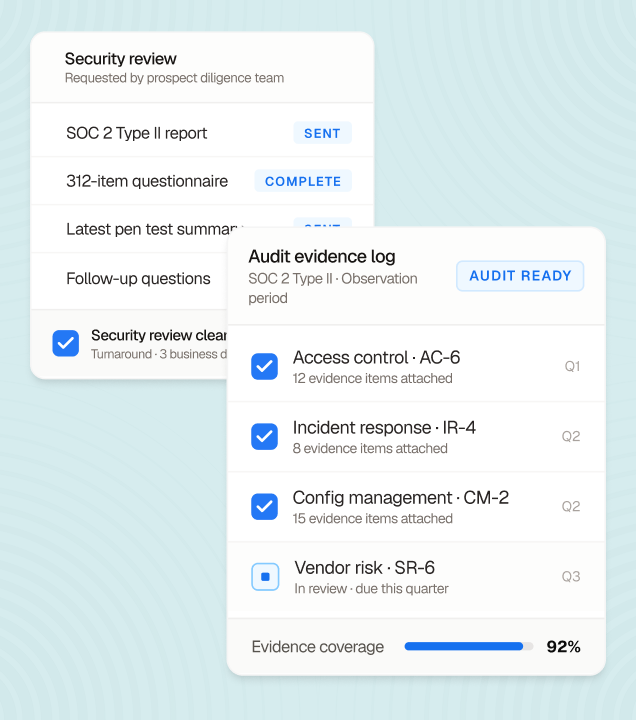
Security spend translates to actual progress.
Auditors, boards, and customers see findings fixed and verified, not a list of problems reopened every year.
Real exploitation, scoped to the risk you actually carry.
Findings come back as remediation guidance your engineers can act on, prioritized by real business risk, not a raw severity dump.
Penetration Testing
Application, cloud, network, API, and AI/LLM testing scoped to the risk you actually carry. Findings come back as remediation guidance your engineers can act on, not a wall of red bars.
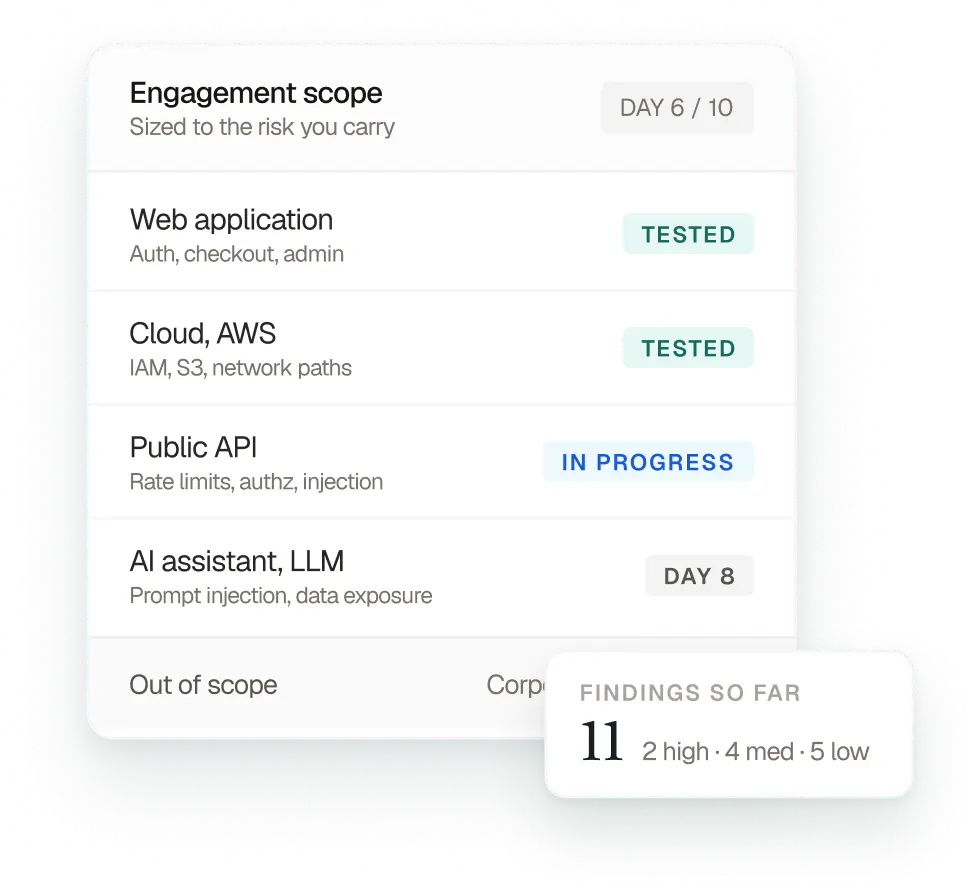
The embedded model. Three steps. No PDFs left behind.
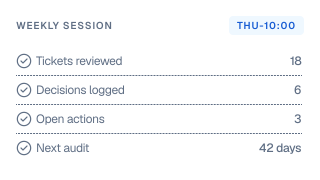
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from the first call to the last.
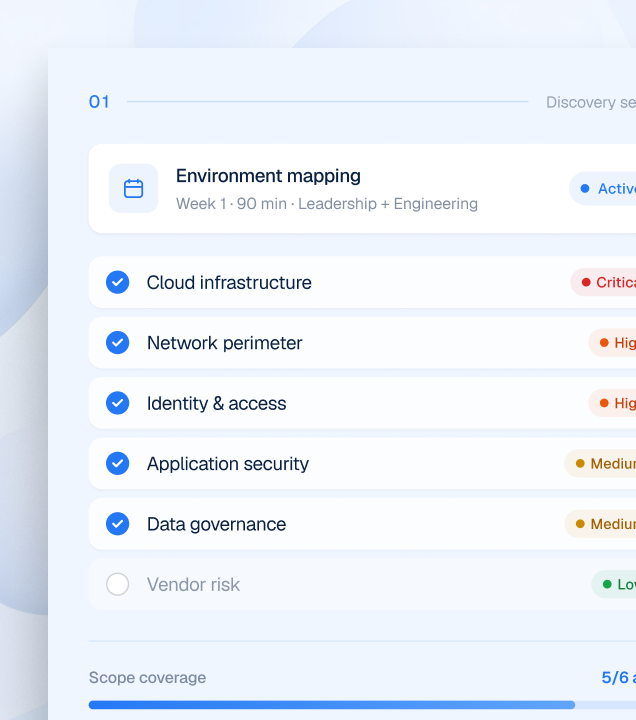
Scope what matters
A working session with your leadership and engineering teams to map your environment, risk priorities, and audit timeline. Not a sales discovery call.
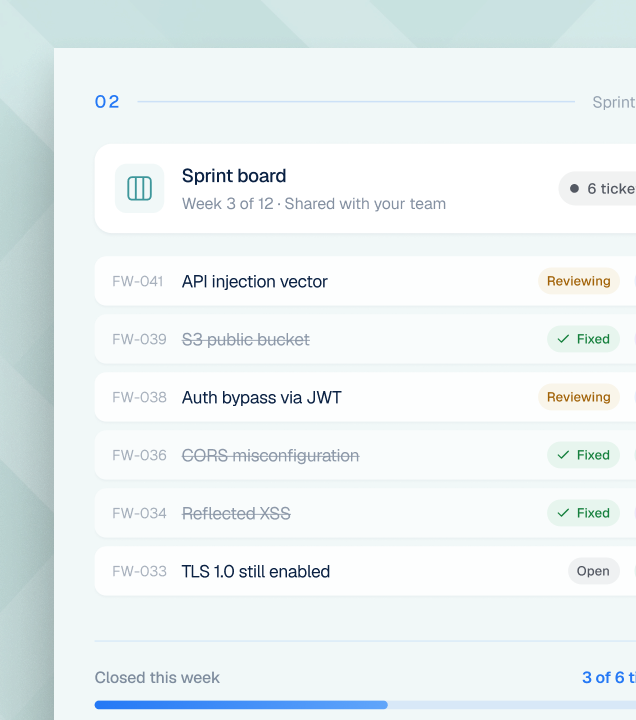
Test like an adversary
Senior engineers exploit findings by hand and chain them the way a real attacker would. You get shared ticketing and same-week visibility, not silence until the report drops.
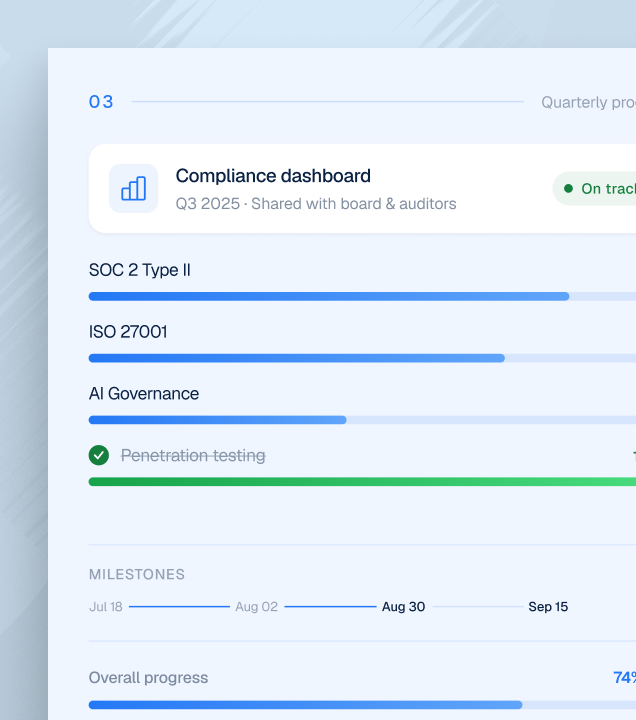
Close the loop
Findings become tickets, tickets become fixes, paired with your team. Then we retest and confirm each one is actually closed, with a clean letter your auditors and customers will accept.
What "expert-led" actually means when you buy a pentest.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.
Expert Practitioners. Regulated-Industry Depth.
Every engagement is led by senior testers with real time in the trenches. 65+ years of combined experience across offensive testing, active incident response, and SOC 2, ISO, and CMMC work.
Responsive On The Timelines That Matter.
Customer deadlines and audit windows don't move. Most engagements kick off within two weeks of signature, and embedded clients get same-day response on critical findings.
Independent And Vendor-Agnostic
We report what we find and recommend what fits your environment, with nothing to upsell. No tool license waiting at the end of the test. Our only product is the work.
Clear Communicators.
You get two reports in one: the exploit path in plain English for your board, and the technical detail your engineers can act on line by line. Plain English is a deliverable, not a nice-to-have.
The work, in the words of the people we did it for.
Six years of engagements across construction, fintech, healthcare, and AI-first companies. A few representative examples.
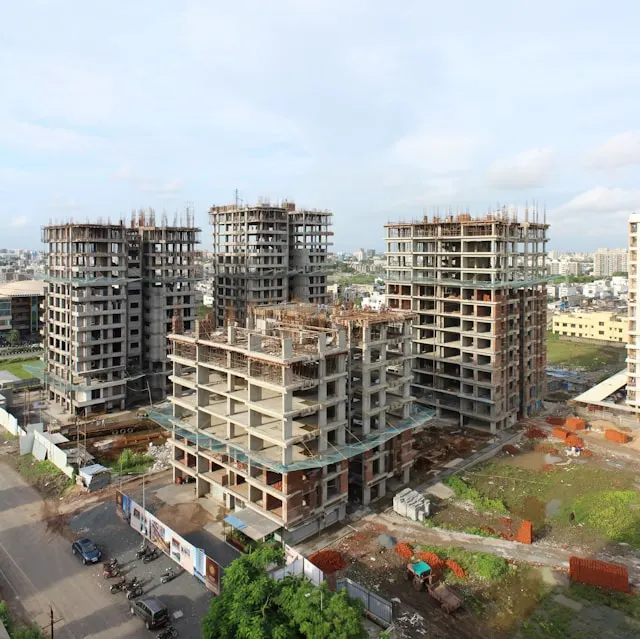
How BZI Construction built a federal-grade cybersecurity program — without hiring a single security employee.
A vCISO engagement delivering NIST 800-171 compliance, CMMC readiness, and real-world protection for a growing construction firm.
A mature vCISO engagement, AI governance included.
The Framework Security–LTK partnership showcases the full power of a mature vCISO engagement — ongoing coverage plus ISO/IEC 42001-aligned AI governance.
A five-year partnership in security, trust, and growth.
A five-year embedded engagement — the kind of retainer relationship the model was designed to sustain.
Built for regulated environments where the answer needs to hold up.
Nine industries. Same model.
Vertical-specific playbooks.


The senior operator on your account is on this page too.
Weekly working sessions with your team. Shared ticketing. Senior engineers assigned to each engagement — the same people from thefirst call to the last.


What senior operators say after we ship.
Four things clients tell us are the actual reason they stay. Vendor independence is the one none of the big firms can match.

"Navigating AI regulation is a moving target. They provided the deep regulatory expertise and proactive guardrails we needed to innovate."

Jeff Neuman, SVP, AI Data & Engineering, Lender Toolkit
"Framework Security establishes a seamless workflow. The team is attentive, communicative, and pragmatic."
Aaron Scruggs, CEO, Rephyr
"If you need to always have a team of go-to security experts, they should be on your shortlist."
Daniel Klingenberg, Information Security Director, Building Zone Industries
"I wish I had found Framework before speaking with any other companies."
Ben Londa, President & CEO, Volo Solutions

"Framework has an uncanny ability to make the highly complex simple to understand."
Tyler Vaughn, Chief Technology Officer, Whitetail Properties
"They know how to execute. They will drill down to find the right solutions to close the gaps and implement that plan."
Jason White, Vice President, HP | Vyopta

Recognized by the industry that grades cybersecurity firms.




Questions teams ask before a pentest
Don't see yours? Send a note — you'll hear back from a real person, usually within a business day.
A scanner tells you what might be vulnerable. We prove what actually is, by exploiting it and chaining findings the way an attacker would. You get the real risk, not a list of maybes.
Web app, cloud (Azure/AWS/GCP), network (external and internal), API, AI/LLM, social engineering, and full red-team adversary simulations. We scope to your environment, not a package.
Yes. Retesting is part of the engagement. We confirm each finding is closed and give you a clean letter you can hand to auditors and customers.
No. We scope rules of engagement with your team up front, coordinate timing, and test safely. You'll know what we're doing and when.
A prioritized findings report with reproduction steps and remediation guidance, an executive summary in plain English, and a post-fix retest letter.
It depends on scope, so we price to your environment instead of publishing a number that fits no one. A focused test runs about a week; larger scopes take longer. Your working session ends with a clear scope and a straight number.
We don't drop a PDF and leave. We embed with your engineers, close the findings with them, and retest to prove it. Firms managing $20B+ in assets trust us, we're a G2 Top 10 firm and Clutch's #1 in North America, and every engagement is senior-led start to finish.
A working session.
Not a sales call.
Bring the environment you need tested, the deadline you're staring at, and the team you have. In 30 minutes we'll tell you honestly whether a pentest is even the right next move, and if it is, how to get started.