See the public exposure.
Review visible services, email authentication and public exposure signals without requiring internal access.
Third parties touch your data, systems and money. Minerva Envoy reviews their public security footprint and helps you focus follow-up on the providers that matter most to your business.



Connect public security signals with your most important third-party relationships.
Prioritize follow-up and revisit the findings on an agreed schedule.
Review visible services, email authentication and public exposure signals without requiring internal access.
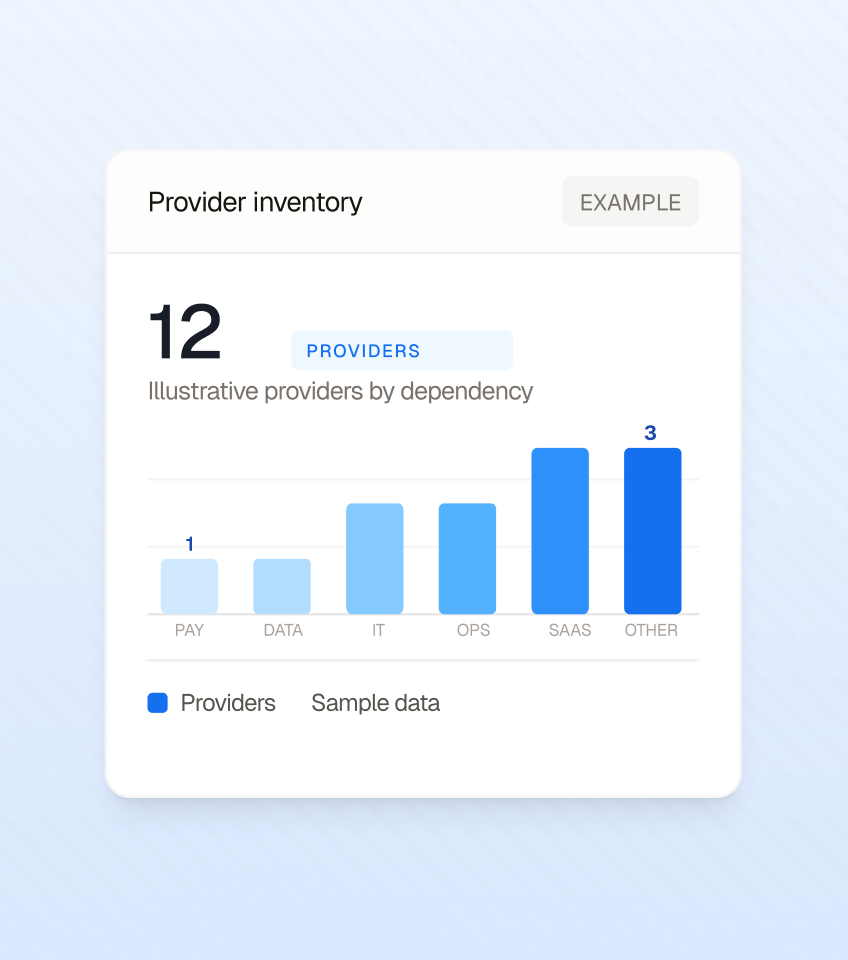
Consider observed risk alongside each provider’s access to your data, systems or money.
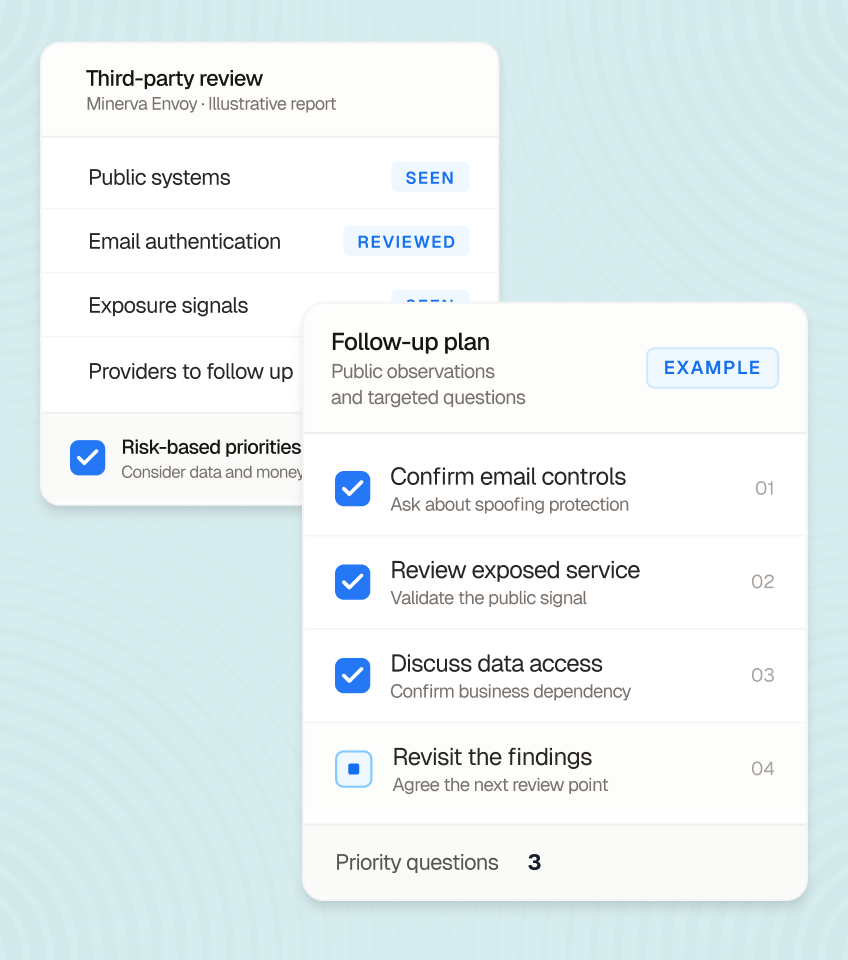
Use targeted questions and recurring reviews to keep third-party risk oversight focused.
An external signal becomes useful when you understand the business dependency behind it. Envoy connects observations with your priorities and the next conversation.
See which providers deserve attention based on public indicators and their importance to your organization.
Give relationship owners specific questions for the providers that warrant review, instead of starting every conversation with a generic survey.
Track findings across scheduled reviews and support evidence of ongoing third-party risk oversight.
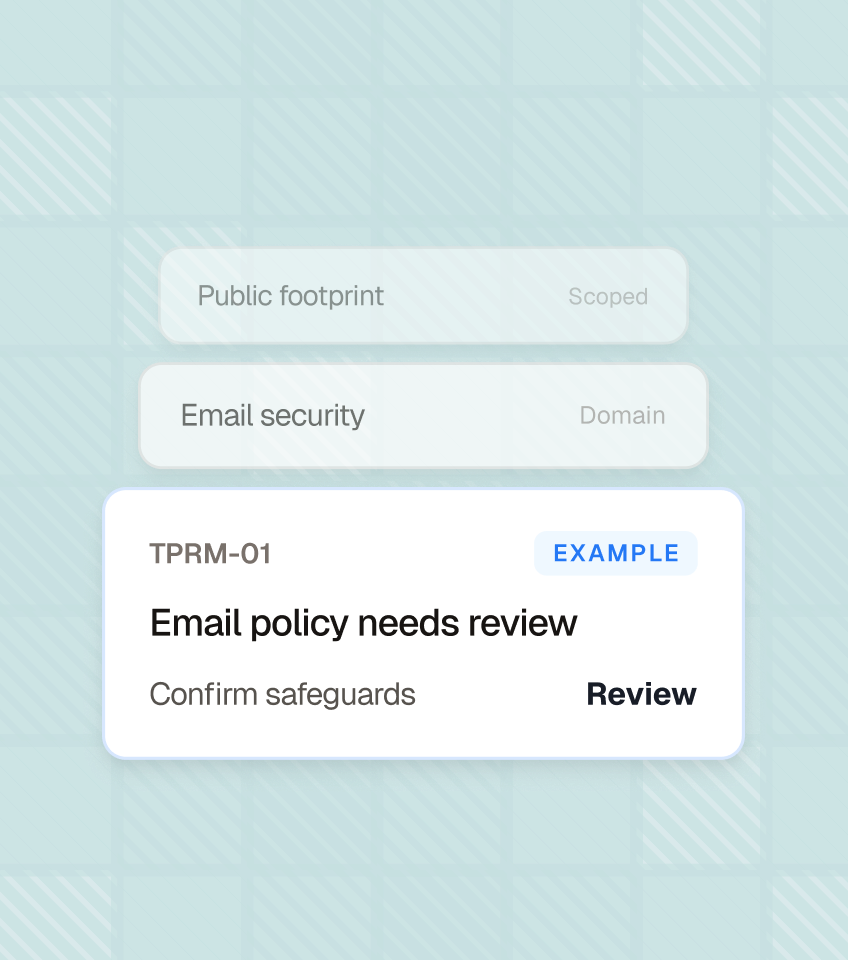
A critical provider’s email policy allows spoofing risk. Confirm its controls before changing payment details.
Framework Security uses passive, non-intrusive review of publicly available information to add an outside perspective to your TPRM program.
Share the providers in scope and explain their access to your data, systems and payment processes.
Assess external security and exposure signals without asking providers to install software or grant internal access.
Review the findings and targeted questions. Agree a recurring schedule to identify changes and keep follow-up focused.
Envoy supports teams managing critical third parties, including regulated organizations that need to document ongoing oversight.
The public-footprint review does not require installations, questionnaires or internal access from the provider. Targeted follow-up can come after the findings are reviewed.
No. It examines publicly visible information. Use those findings alongside due diligence, contractual requirements and evidence supplied by the provider.
Reviews run on an agreed recurring schedule. Findings reflect what is visible at those review points, rather than continuous, real-time detection.
The report can support your record of third-party risk monitoring and follow-up. It does not certify a provider’s security or replace your organization’s oversight responsibilities.
MINERVA ENVOY
Bring your critical provider list to a working session. Framework Security will help define the scope and cadence for Envoy.
Senior-led, embedded cybersecurityfor regulated teams.