See what’s connected.
Discover responding hosts and open services across the networks in your agreed scope.
You can’t make informed security decisions with an incomplete picture of your network. Minerva Recon turns scoped network scans into an evidence-backed inventory your team can use.



See responding hosts, open services and likely applications across your scoped network.
Get the evidence your team needs to investigate and act.
Discover responding hosts and open services across the networks in your agreed scope.
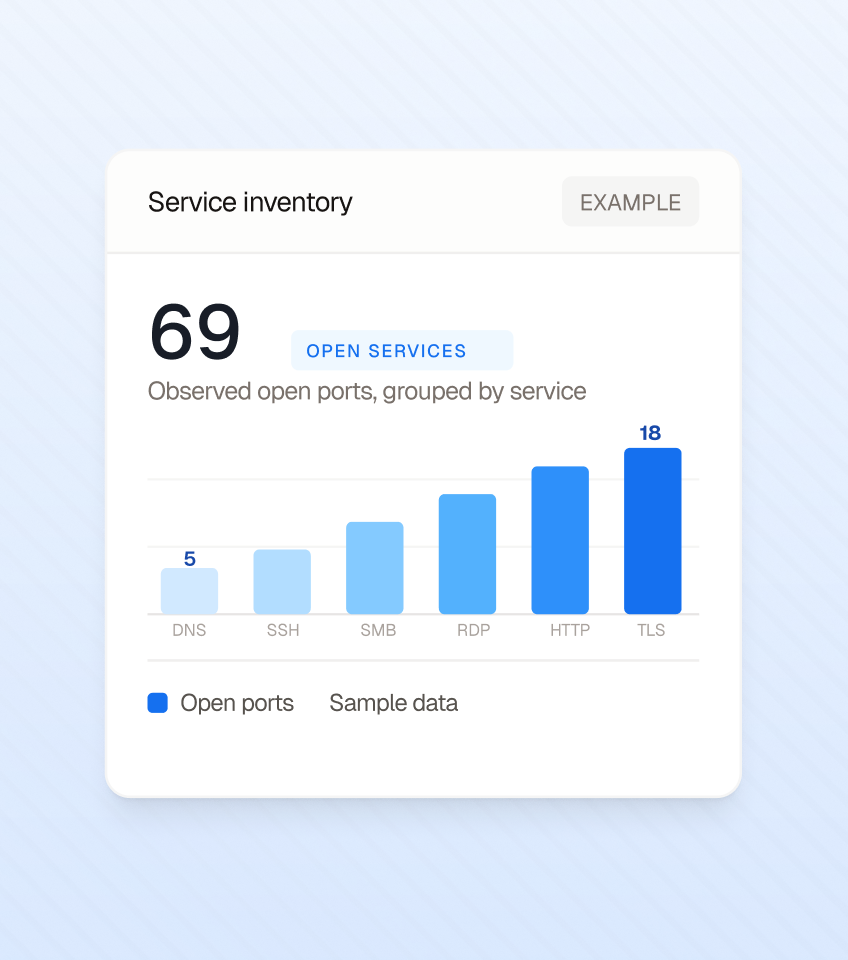
Review the services behind open ports and decide which access needs a closer look.
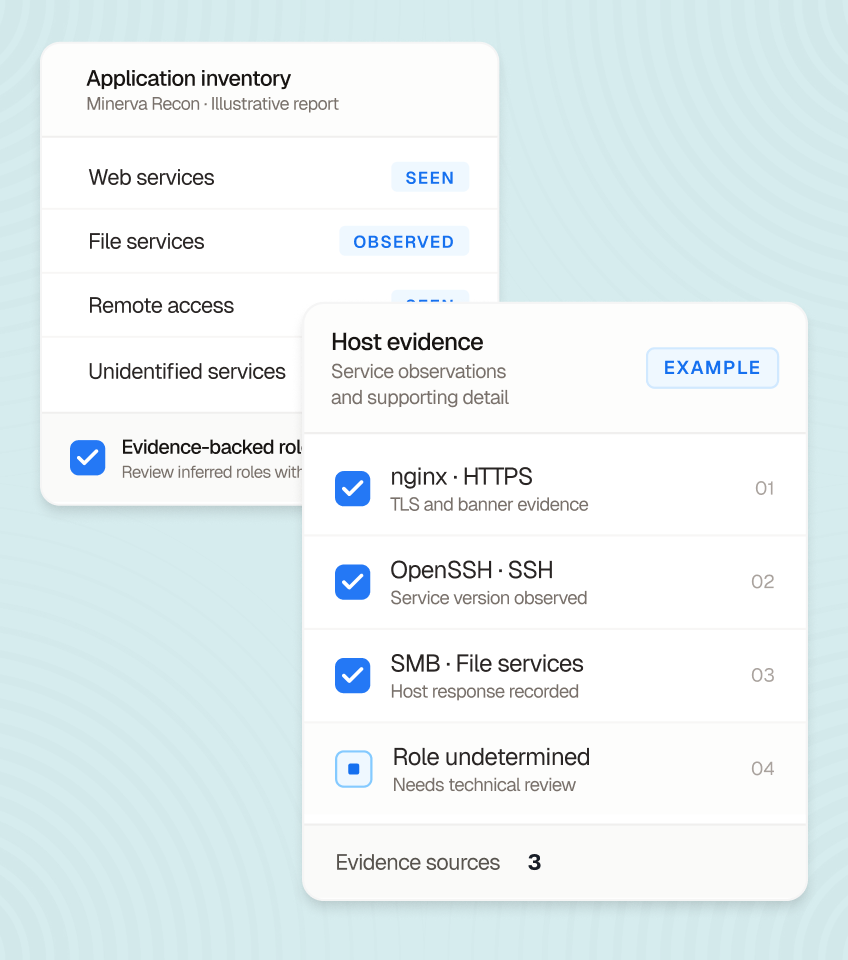
Identify likely applications and server roles, with per-host evidence to support the findings.
Leadership needs the context. Technical teams need the detail. Recon brings both into a single report, with the observations behind the conclusions.
Understand the network picture, key observations and areas that merit a closer look.
Review discovered hosts, services, applications and server roles, with vendor and product summaries.
Trace observations to per-host evidence and scan records, so technical teams have a starting point for validation.
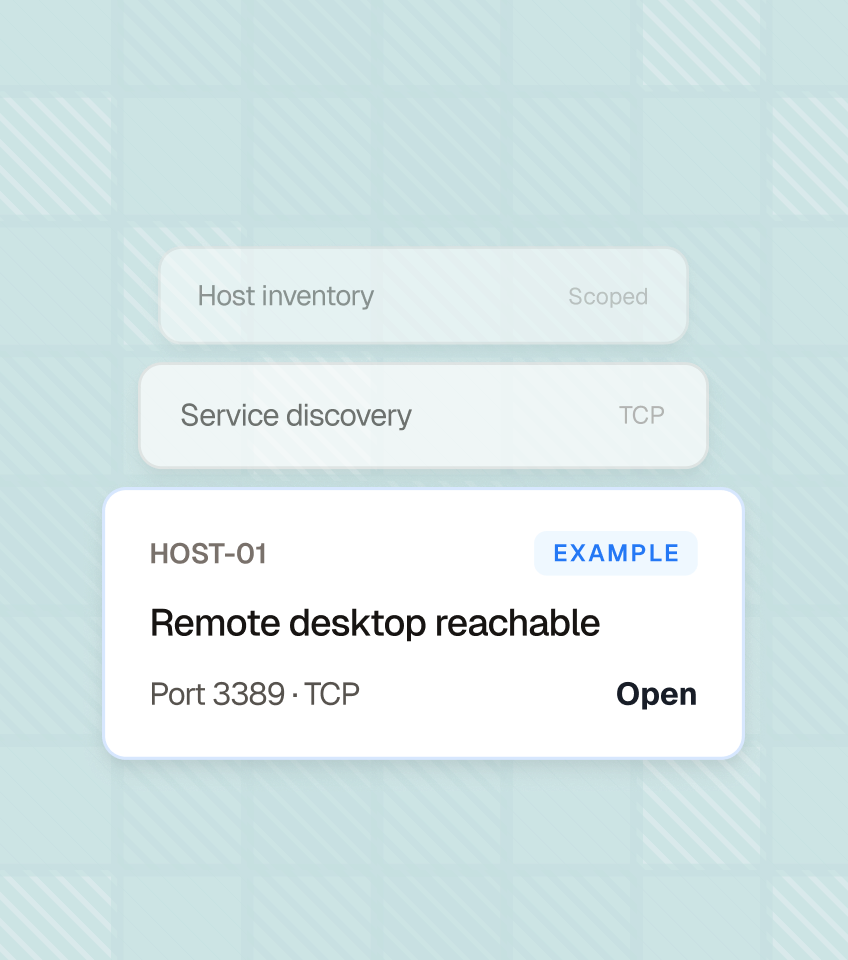
Remote desktop is reachable. Confirm access is restricted to approved users and networks.
Framework Security sets the assessment scope with you. Recon gathers the network evidence and uses AI-assisted analysis to determine where a closer look could help.
Define the networks, addresses and hostnames to assess. Confirm the access needed to reach each environment and the boundaries of the work.
Run baseline discovery, then use bounded follow-up scans to examine relevant services. AI-generated observations are checked against collected evidence.
Work with Framework Security to interpret the report and decide what deserves further investigation or a change to your security plan.
Offices, data centers and reachable cloud networks are natural starting points. Coverage depends on the networks Recon can access and the scope you agree with Framework Security.
Yes. Each network needs a reachable scan point. Connected sites may be accessible through a VPN; disconnected environments may need a local deployment.
If there is no shared or reachable network, network discovery may offer limited value. Framework Security can help identify which Minerva product fits the exposure you need to understand.
Recon provides network discovery, inventory and evidence-backed observations. A penetration test examines exploitability in greater depth and is a separate scope of work.
Repeat scans can be arranged to refresh the inventory. The cadence and coverage are agreed for your environment; Recon does not imply continuous monitoring.
MINERVA RECON
Talk through your environment with Framework Security. We’ll help define where Recon can give your team useful visibility.
Senior-led, embedded cybersecurityfor regulated teams.