Understand the business impact.
Give leadership a plain-English view of the findings, their implications and the priorities competing for time and budget.
Minerva Insights turns security assessment evidence into business context, technical findings and remediation priorities. Give leadership and IT a shared basis for deciding what to address next.



Bring business context and technical detail into the same conversation.
Use one assessment record to agree what needs attention next.
Give leadership a plain-English view of the findings, their implications and the priorities competing for time and budget.
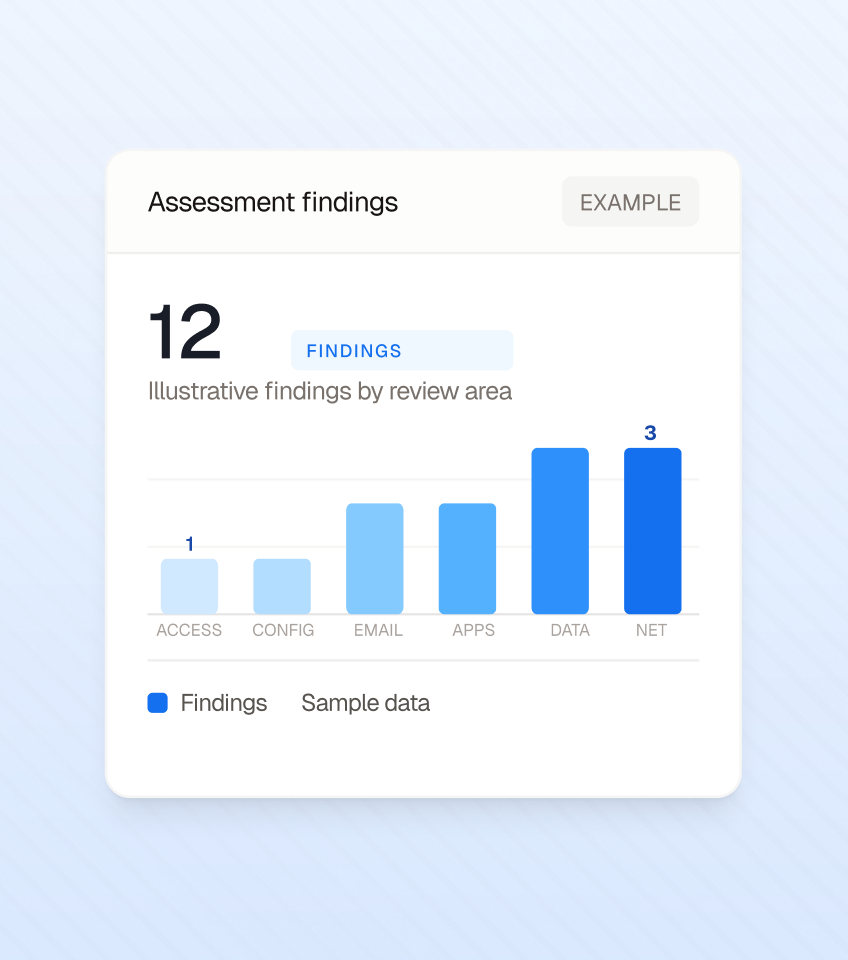
Trace findings back to collected observations. Examine reported attack chains where the underlying evidence supports each step.
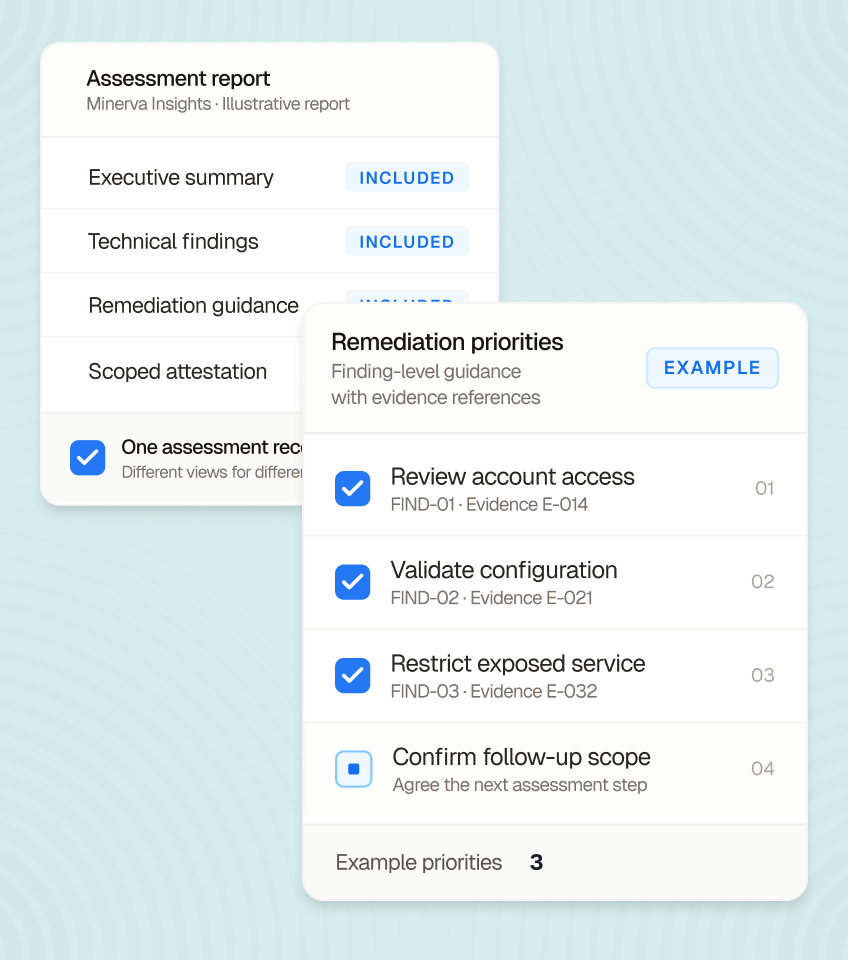
Bring remediation guidance into the planning discussion, so leadership and IT can agree priorities from the same record.
A report should help you allocate time and budget. Insights connects the leadership narrative to the technical record, so both teams can work from the same findings.
Understand what the assessment found, why it matters to the business and where attention belongs.
Review structured findings, severity, affected assets and evidence references. Machine-readable findings and evidence can accompany the agreed deliverables.
Where agreed, a separate letter of attestation summarizes the assessment without exposing sensitive technical detail. It is not a security guarantee or compliance certification.
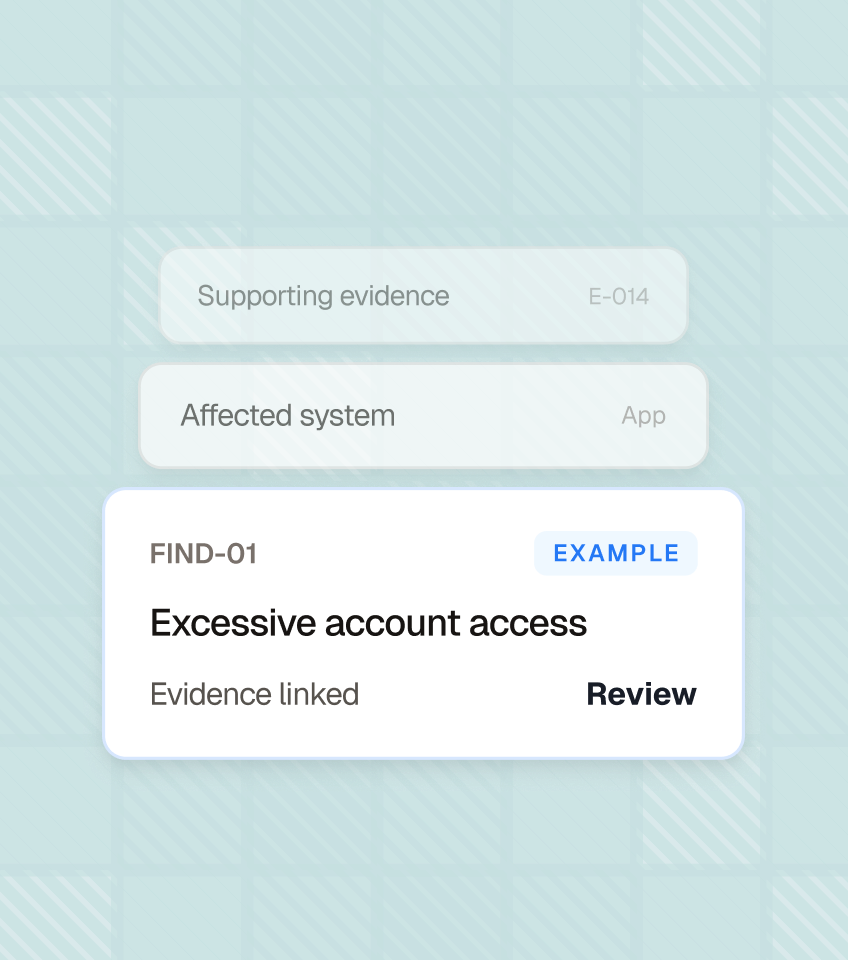
Evidence E-014 supports this finding. Review account access before planning the fix.
Insights is the reporting layer behind Minerva Recon, Minerva Shield and penetration testing engagements. The underlying assessments collect the evidence; Insights organizes and explains it.
Bring scoped assessment results into a consistent record of findings, severity and affected assets. Consolidate duplicates and retain evidence identifiers.
Use AI to explain findings, examine supported attack chains and develop remediation priorities. Check generated claims and reported chain steps against the evidence.
Build the executive summary, technical findings and remediation guidance from the same record. Include a separate scoped attestation where agreed.
Use Insights when leadership needs to understand the business implications and technical teams need evidence and practical guidance to plan the work.
No. Insights is Framework Security’s AI reporting agent. It works from evidence collected through a scoped assessment; it does not replace the underlying network discovery, identity analysis or penetration testing.
AI helps interpret findings, explain business implications and develop remediation priorities. Structured findings come first, and AI-generated claims are checked against supporting evidence.
Deliverables depend on the engagement scope. They can include an executive summary, detailed technical report, remediation guidance, machine-readable findings and evidence, and a separate letter of attestation.
No. Insights supports assessment and remediation decisions. It does not automatically fix issues, and an attestation relates only to the scoped assessment; it is not a security guarantee or compliance certification.
MINERVA INSIGHTS
Talk with Framework Security about your assessment scope and the reporting your leadership and technical teams need.
Senior-led, embedded cybersecurityfor regulated teams.