See the AI tools in use.
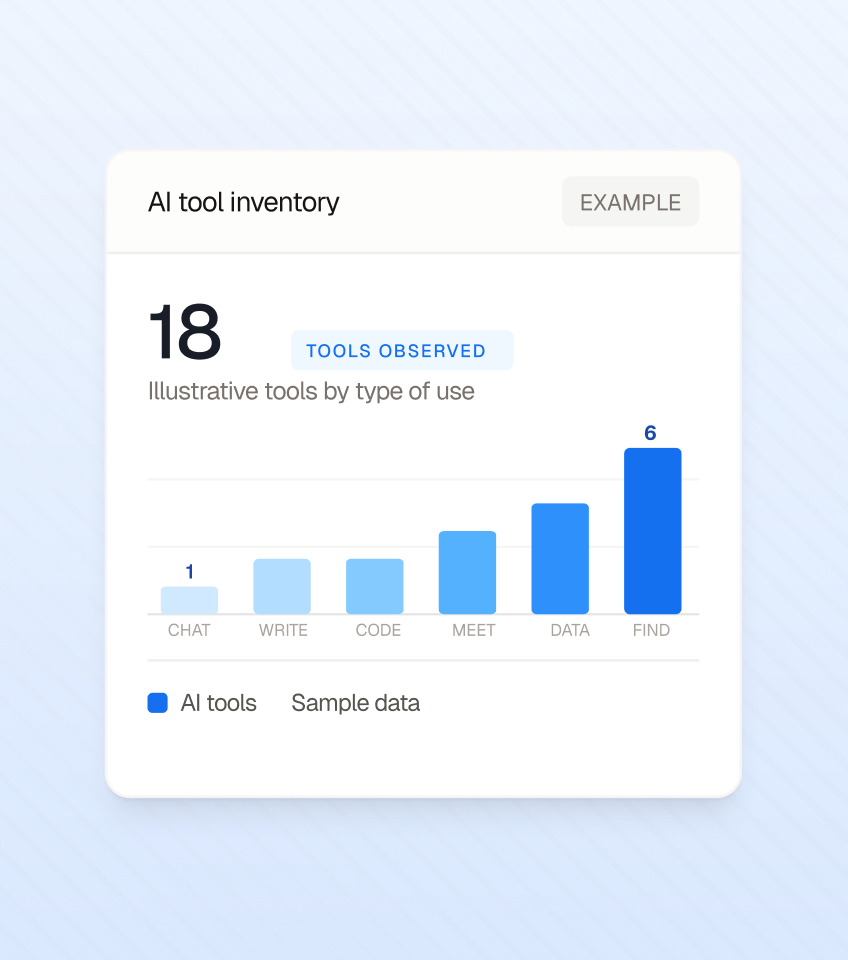
Identify visible AI applications and assistants, including tools outside the approved list.
AI assistants can gain access to company information before the rules are clear. Minerva Lantern identifies visible AI use, examines data access and gives leadership a practical starting point for governance.



Connect visible AI use with the company information those tools can access.
Give leadership a practical starting point for approvals, controls and policy.
Identify visible AI applications and assistants, including tools outside the approved list.
Review access to company mail, files, calendars and code, and assess where sensitive information may be exposed.
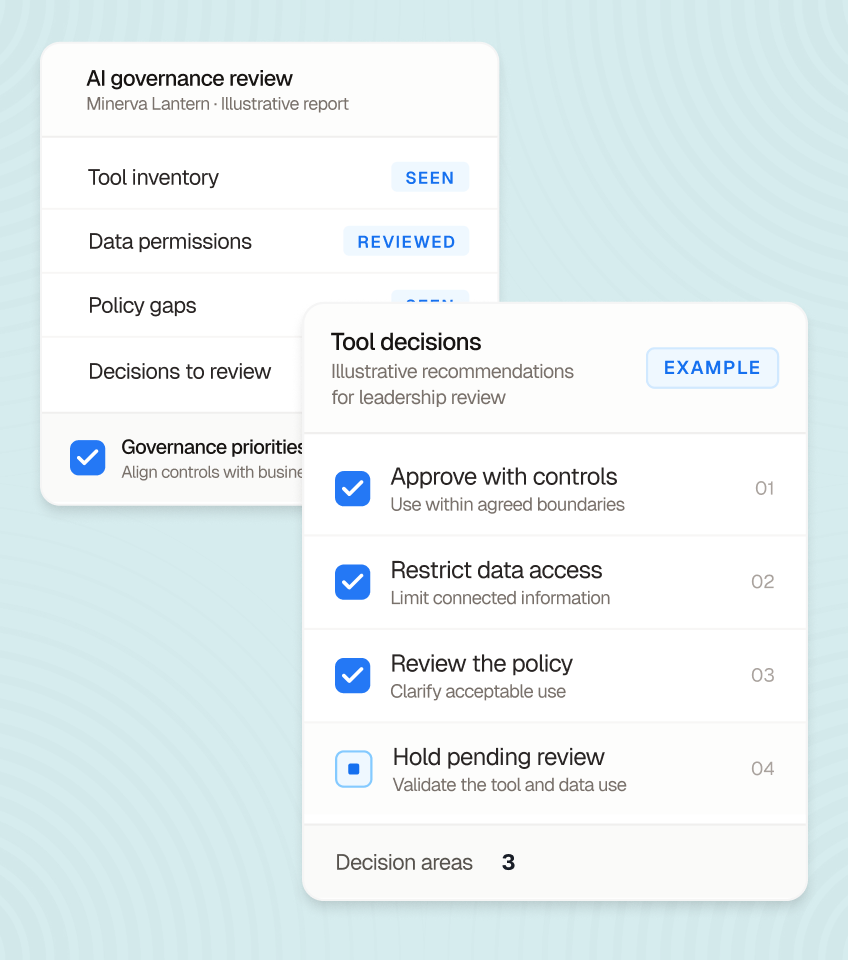
Review tools to approve, restrict or block, alongside policy gaps and a practical governance roadmap.
Your team needs more than a list of AI applications. Lantern helps leadership decide which uses to support, which need limits and where stronger controls belong.
Bring visible tools, available adoption information and connected data sources into a report leadership can discuss.
Review a focused list of tools to approve, restrict or block, with the risk context behind those recommendations.
Connect findings to ISO 42001 and the NIST AI Risk Management Framework, with relevant FINRA guidance considered for financial services clients.
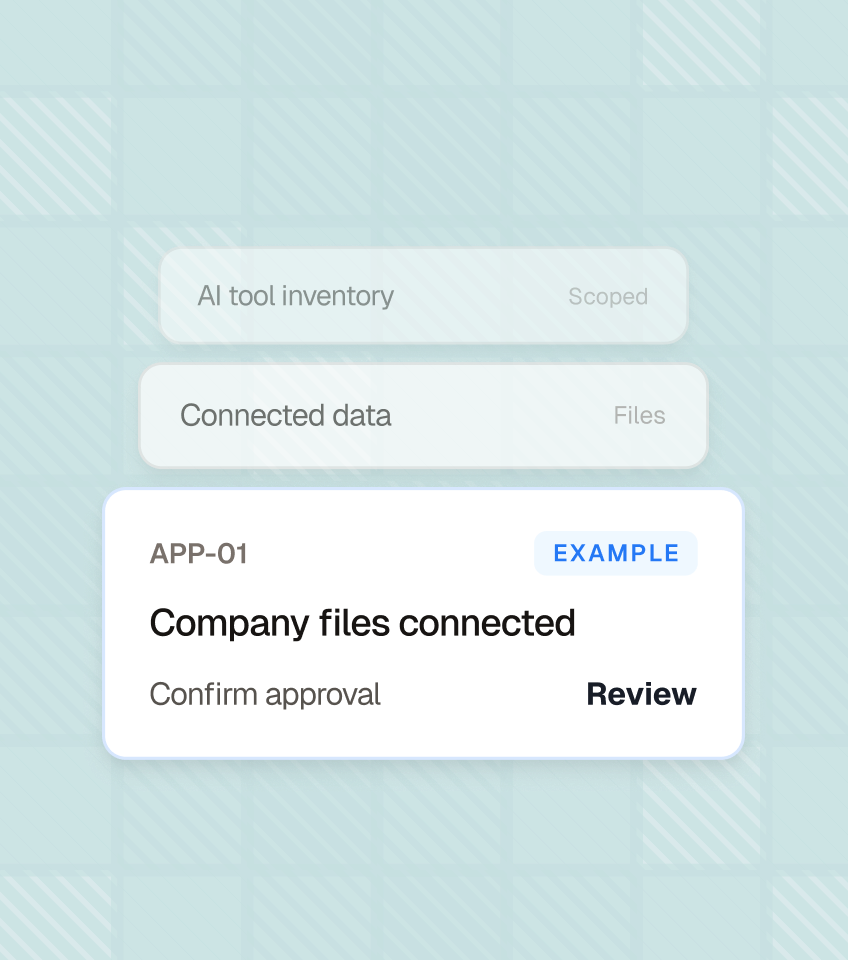
An AI assistant has access to company files. Confirm the data scope and approval before expanding use.
Framework Security combines technical observations with your business context, so recommendations reflect how your team needs to work.
Discuss AI use, sensitive information and leadership expectations. Agree the identity, email and SaaS sources available for review.
Identify visible AI applications, assess permissions and likely data exposure, and compare those findings with existing policy.
Review tool-level recommendations and a governance roadmap with Framework Security. Decide which controls and policy changes to prioritize.
Lantern fits organizations that want clearer oversight of AI adoption, whether they are writing their first policy or reviewing existing controls.
Coverage depends on the systems and evidence available. Lantern identifies visible tool use and likely data exposure; it does not claim to observe every prompt or personal account.
No. The review can identify policy gaps and provide a starting point for acceptable-use rules and oversight.
No. Framework mappings support governance planning. The assessment itself does not certify your organization or establish compliance.
Lantern provides recommendations to approve, restrict or block. Your organization decides how to implement those choices with the appropriate owners.
MINERVA LANTERN
Talk through the tools your team uses and the information you need to protect. Framework Security will help scope a Lantern review.
Senior-led, embedded cybersecurityfor regulated teams.